Part X, section 36

Information security compliance

Access restriction regimes, trade secrets, the IS system, DLP and correspondence

  • 35 slides
  • 6 subsections
  • Edition of 25 October 2026

36.1

Access restriction regimes

Which secrets the law recognises and how access is restricted

ZIN-001

Secrecy is protected by regime, processes and evidence

Cost of error in 2025-2026 figures and the key question
Slide ZIN-001: Secrecy is protected by regime, processes and evidence
Slide text

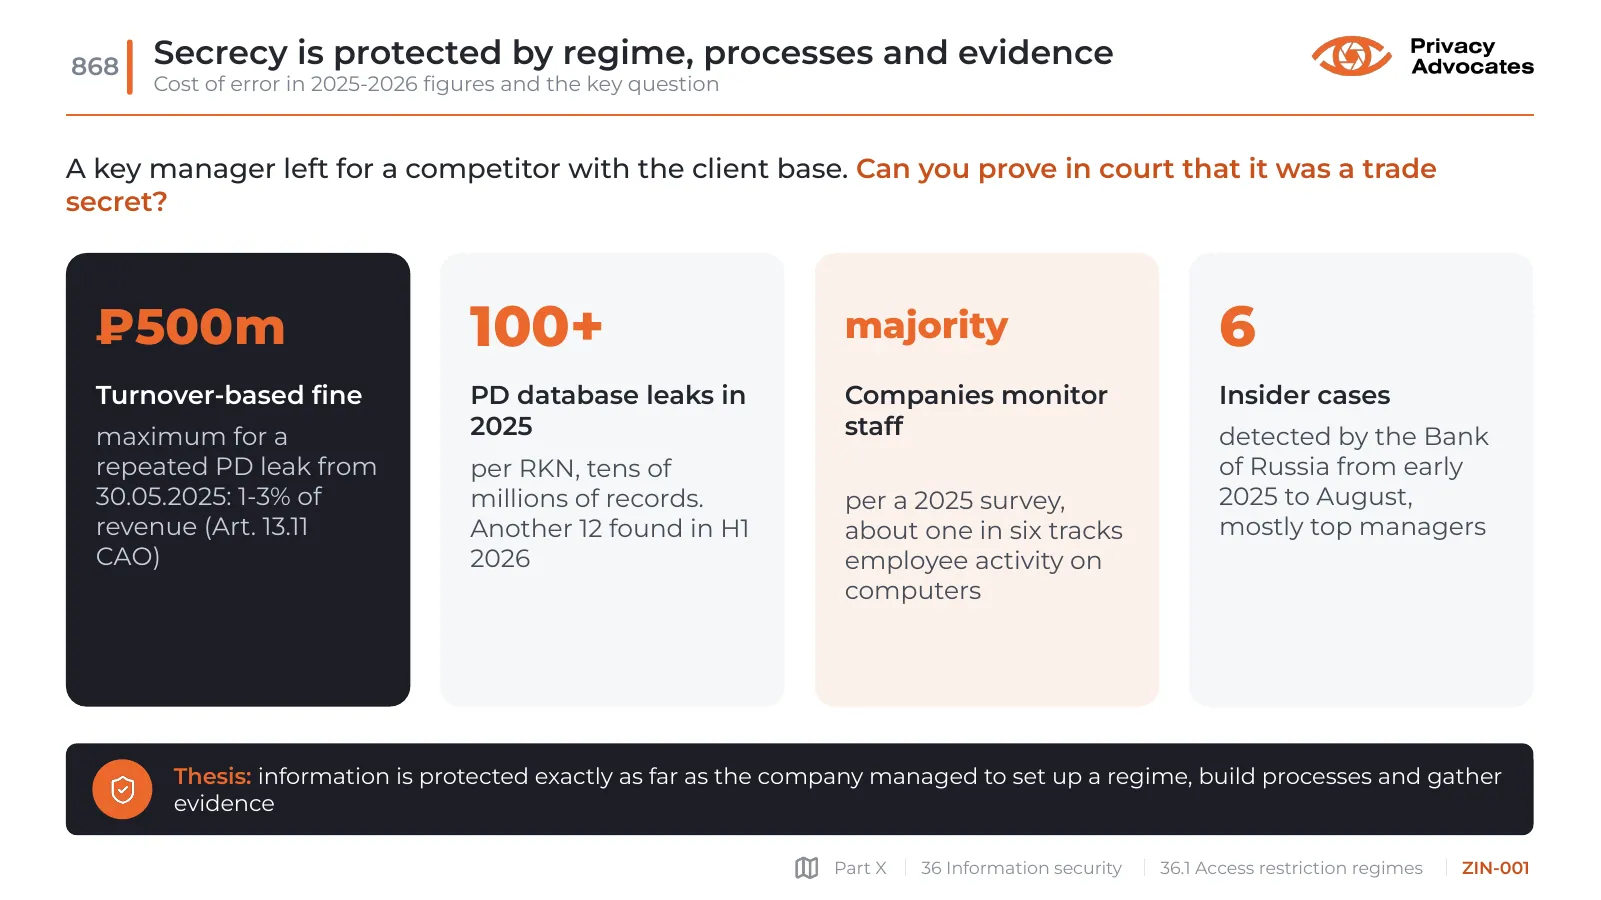
A key manager left for a competitor with the client base. Can you prove in court that it was a trade secret?

₽500m

Turnover-based fine

maximum for a repeated PD leak from 30.05.2025: 1-3% of revenue (Art. 13.11 CAO)

100+

PD database leaks in 2025

per RKN, tens of millions of records. Another 12 found in H1 2026

majority

Companies monitor staff

per a 2025 survey, about one in six tracks employee activity on computers

6

Insider cases

detected by the Bank of Russia from early 2025 to August, mostly top managers

Thesis: information is protected exactly as far as the company managed to set up a regime, build processes and gather evidence
ZIN-002

Alfa-Soft case: trade secret regime, insider info, DLP

Fictional IT company: 300 staff, retail SaaS, exchange-listed bonds

Slide ZIN-002: Alfa-Soft case: trade secret regime, insider info, DLP
Slide text
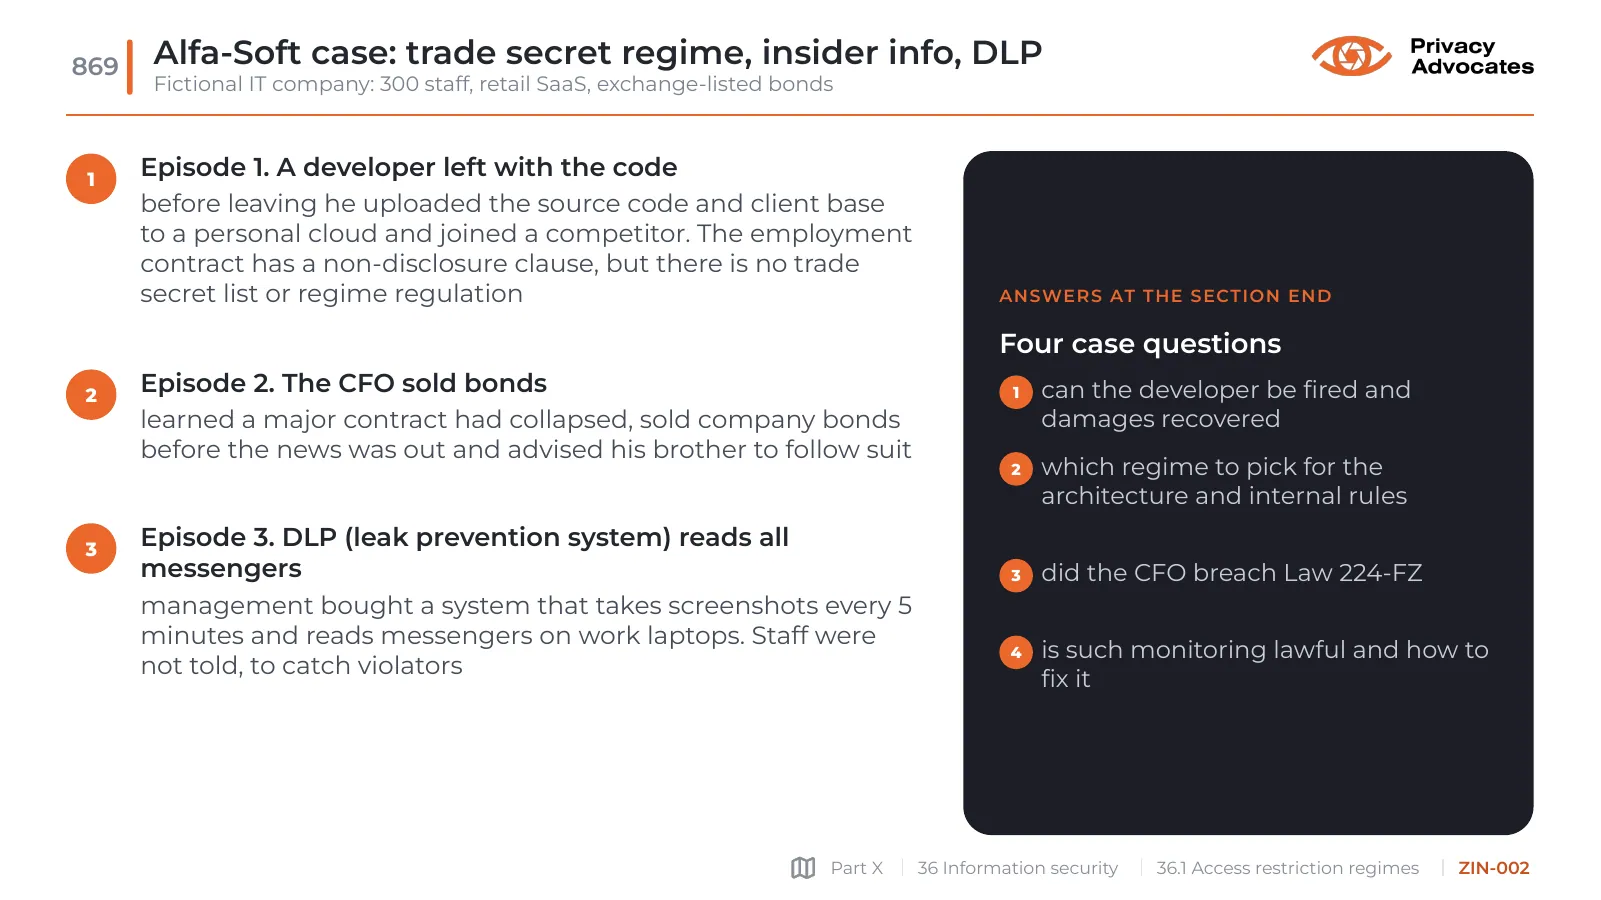
  • 1
  • Episode 1. A developer left with the code

before leaving he uploaded the source code and client base to a personal cloud and joined a competitor. The employment contract has a non-disclosure clause, but there is no trade secret list or regime regulation

  • 2
  • Episode 2. The CFO sold bonds

learned a major contract had collapsed, sold company bonds before the news was out and advised his brother to follow suit

  • 3
  • Episode 3. DLP (leak prevention system) reads all messengers

management bought a system that takes screenshots every 5 minutes and reads messengers on work laptops. Staff were not told, to catch violators

Answers at the section end

Four case questions

  • 1
  • can the developer be fired and damages recovered
  • 2
  • which regime to pick for the architecture and internal rules
  • 3
  • did the CFO breach Law 224-FZ
  • 4
  • is such monitoring lawful and how to fix it
ZIN-003

Access is restricted by law or by the holder's decision

Art. 5 of 149-FZ splits information into public and restricted

Slide ZIN-003: Access is restricted by law or by the holder's decision
Slide text

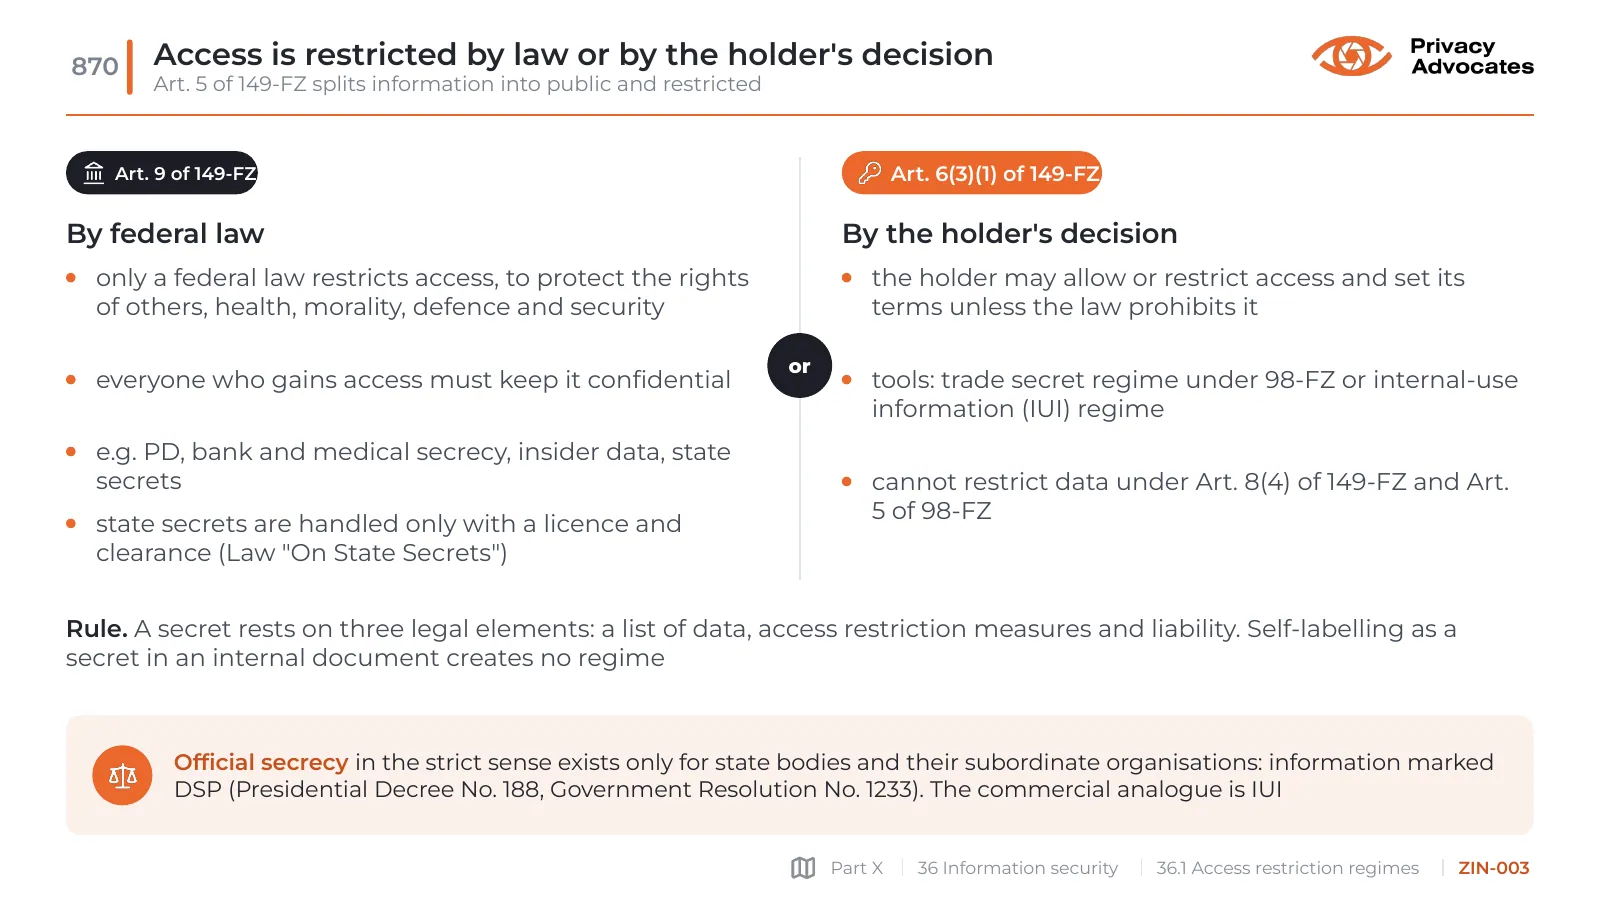
or

Art. 9 of 149-FZ

By federal law

only a federal law restricts access, to protect the rights of others, health, morality, defence and security

everyone who gains access must keep it confidential

e.g. PD, bank and medical secrecy, insider data, state secrets

state secrets are handled only with a licence and clearance (Law "On State Secrets")

Art. 6(3)(1) of 149-FZ

By the holder's decision

the holder may allow or restrict access and set its terms unless the law prohibits it

tools: trade secret regime under 98-FZ or internal-use information (IUI) regime

cannot restrict data under Art. 8(4) of 149-FZ and Art. 5 of 98-FZ

Rule. A secret rests on three legal elements: a list of data, access restriction measures and liability. Self-labelling as a secret in an internal document creates no regime

Official secrecy in the strict sense exists only for state bodies and their subordinate organisations: information marked DSP (Presidential Decree No. 188, Government Resolution No. 1233). The commercial analogue is IUI

ZIN-004

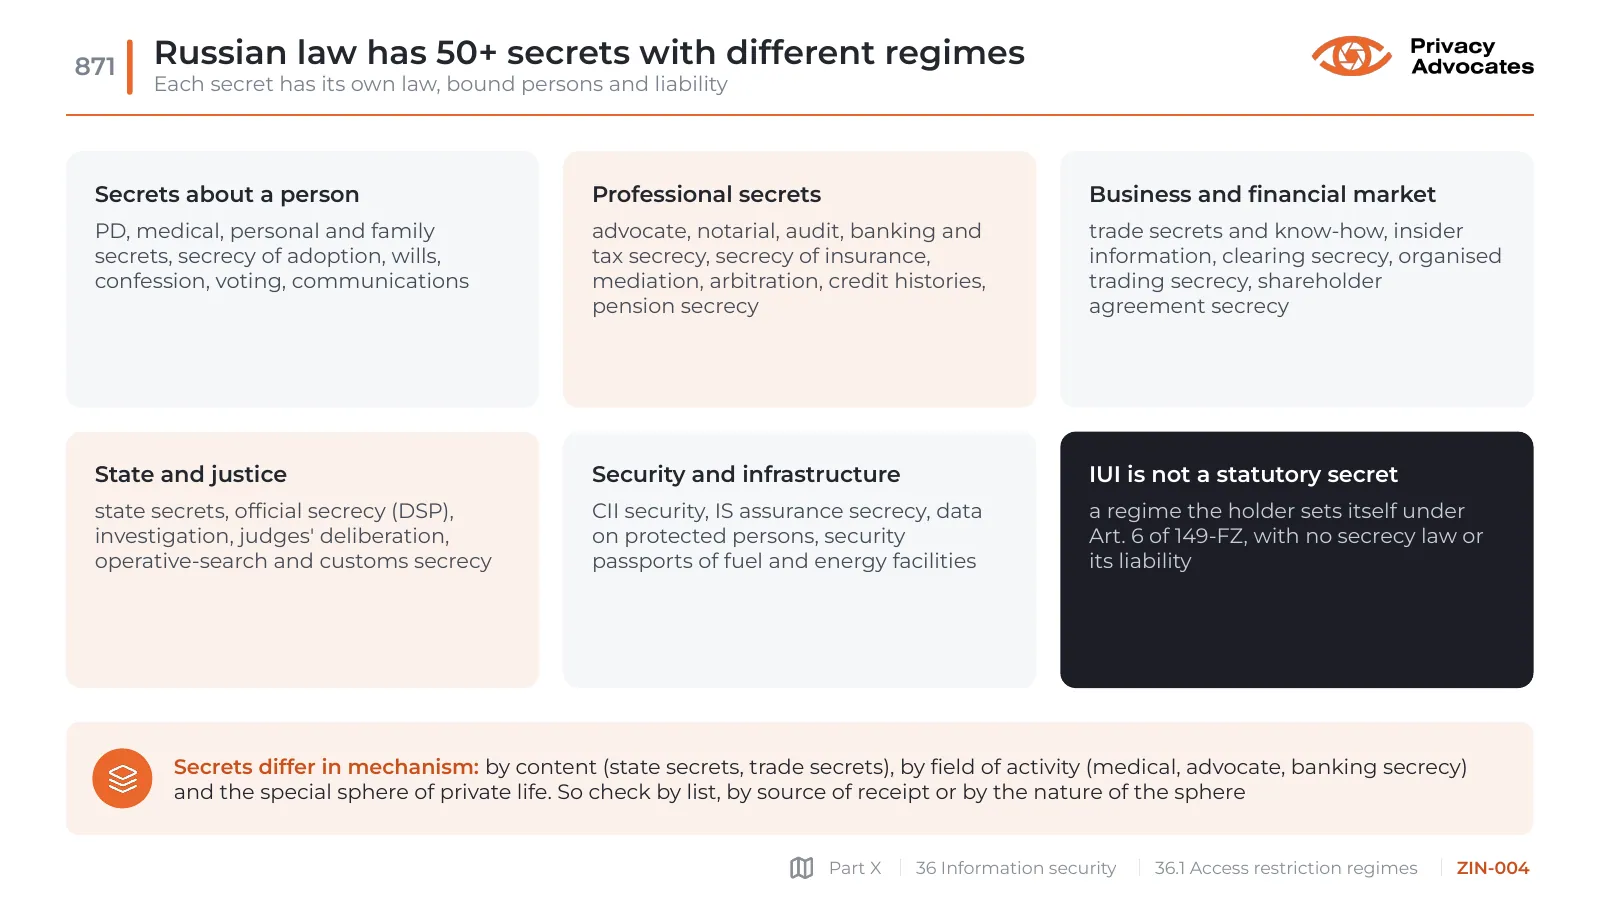
Russian law has 50+ secrets with different regimes

Each secret has its own law, bound persons and liability

Slide ZIN-004: Russian law has 50+ secrets with different regimes
Slide text

Secrets about a person

PD, medical, personal and family secrets, secrecy of adoption, wills, confession, voting, communications

Professional secrets

advocate, notarial, audit, banking and tax secrecy, secrecy of insurance, mediation, arbitration, credit histories, pension secrecy

Business and financial market

trade secrets and know-how, insider information, clearing secrecy, organised trading secrecy, shareholder agreement secrecy

State and justice

state secrets, official secrecy (DSP), investigation, judges' deliberation, operative-search and customs secrecy

Security and infrastructure

CII security, IS assurance secrecy, data on protected persons, security passports of fuel and energy facilities

IUI is not a statutory secret

a regime the holder sets itself under Art. 6 of 149-FZ, with no secrecy law or its liability

Secrets differ in mechanism: by content (state secrets, trade secrets), by field of activity (medical, advocate, banking secrecy) and the special sphere of private life. So check by list, by source of receipt or by the nature of the sphere

ZIN-005

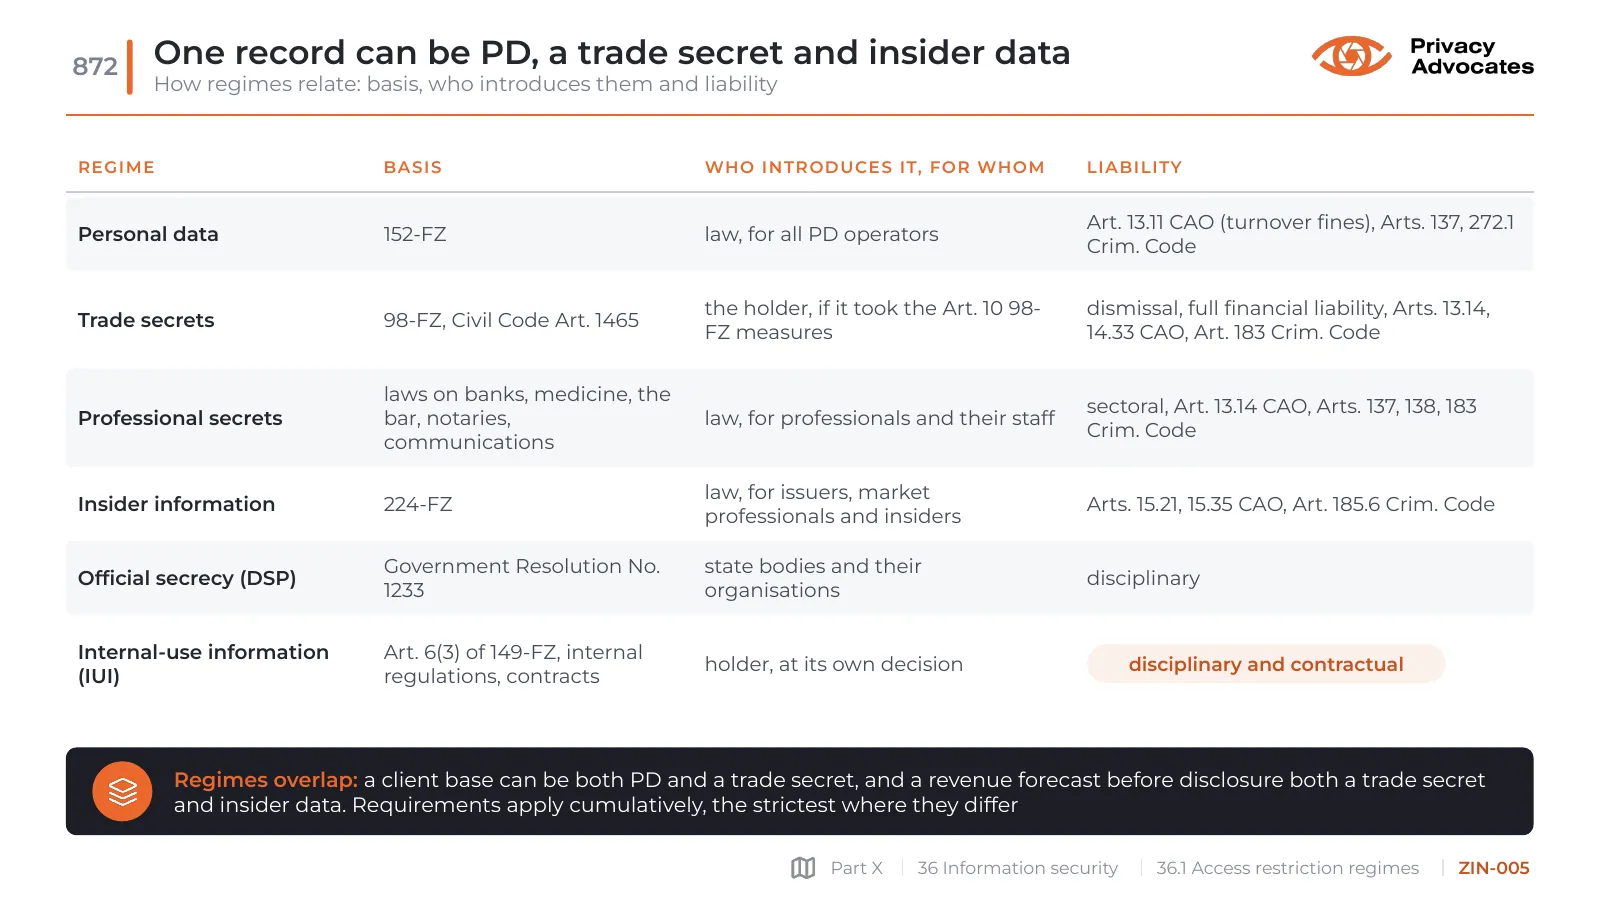
One record can be PD, a trade secret and insider data

How regimes relate: basis, who introduces them and liability

Slide ZIN-005: One record can be PD, a trade secret and insider data
Slide text
  • Regime
  • Basis
  • Who introduces it, for whom
  • Liability
  • Personal data
  • 152-FZ
  • law, for all PD operators
  • Art. 13.11 CAO (turnover fines), Arts. 137, 272.1 Crim. Code
  • Trade secrets
  • 98-FZ, Civil Code Art. 1465
  • the holder, if it took the Art. 10 98-FZ measures
  • dismissal, full financial liability, Arts. 13.14, 14.33 CAO, Art. 183 Crim. Code
  • Professional secrets
  • laws on banks, medicine, the bar, notaries, communications
  • law, for professionals and their staff
  • sectoral, Art. 13.14 CAO, Arts. 137, 138, 183 Crim. Code
  • Insider information
  • 224-FZ
  • law, for issuers, market professionals and insiders
  • Arts. 15.21, 15.35 CAO, Art. 185.6 Crim. Code
  • Official secrecy (DSP)
  • Government Resolution No. 1233
  • state bodies and their organisations
  • disciplinary
  • Internal-use information (IUI)
  • Art. 6(3) of 149-FZ, internal regulations, contracts
  • holder, at its own decision
  • disciplinary and contractual

Regimes overlap: a client base can be both PD and a trade secret, and a revenue forecast before disclosure both a trade secret and insider data. Requirements apply cumulatively, the strictest where they differ

ZIN-006

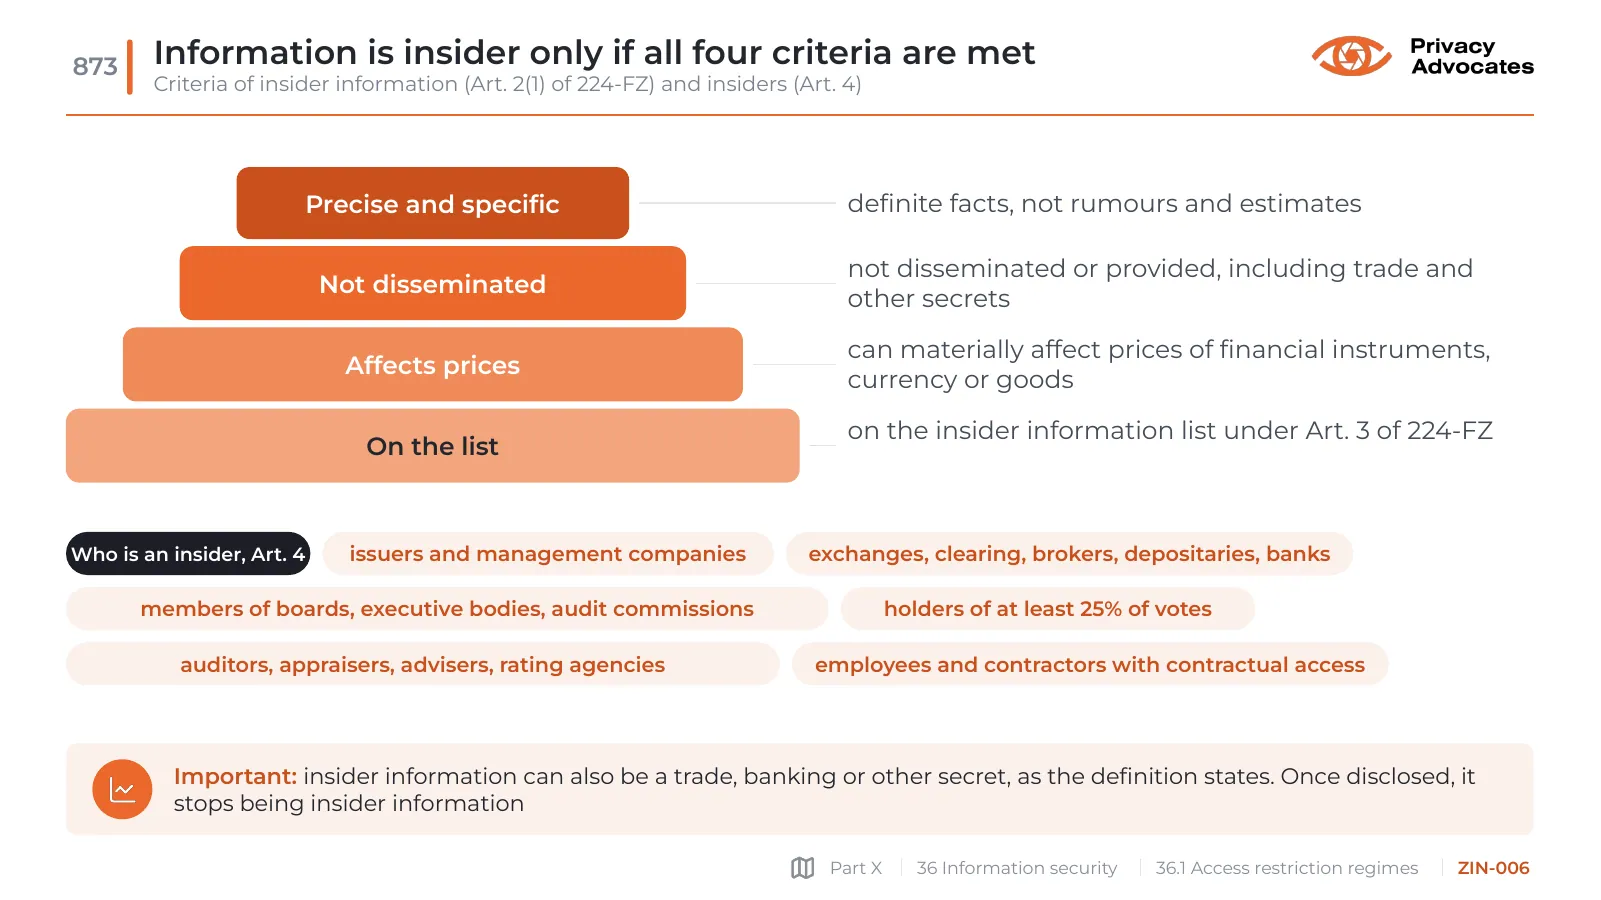
Information is insider only if all four criteria are met

Criteria of insider information (Art. 2(1) of 224-FZ) and insiders (Art. 4)

Slide ZIN-006: Information is insider only if all four criteria are met
Slide text
  • Precise and specific
  • definite facts, not rumours and estimates
  • Not disseminated
  • not disseminated or provided, including trade and other secrets
  • Affects prices
  • can materially affect prices of financial instruments, currency or goods
  • On the list
  • on the insider information list under Art. 3 of 224-FZ
  • Who is an insider, Art. 4
  • issuers and management companies
  • exchanges, clearing, brokers, depositaries, banks
  • members of boards, executive bodies, audit commissions
  • holders of at least 25% of votes
  • auditors, appraisers, advisers, rating agencies
  • employees and contractors with contractual access

Important: insider information can also be a trade, banking or other secret, as the definition states. Once disclosed, it stops being insider information

ZIN-007

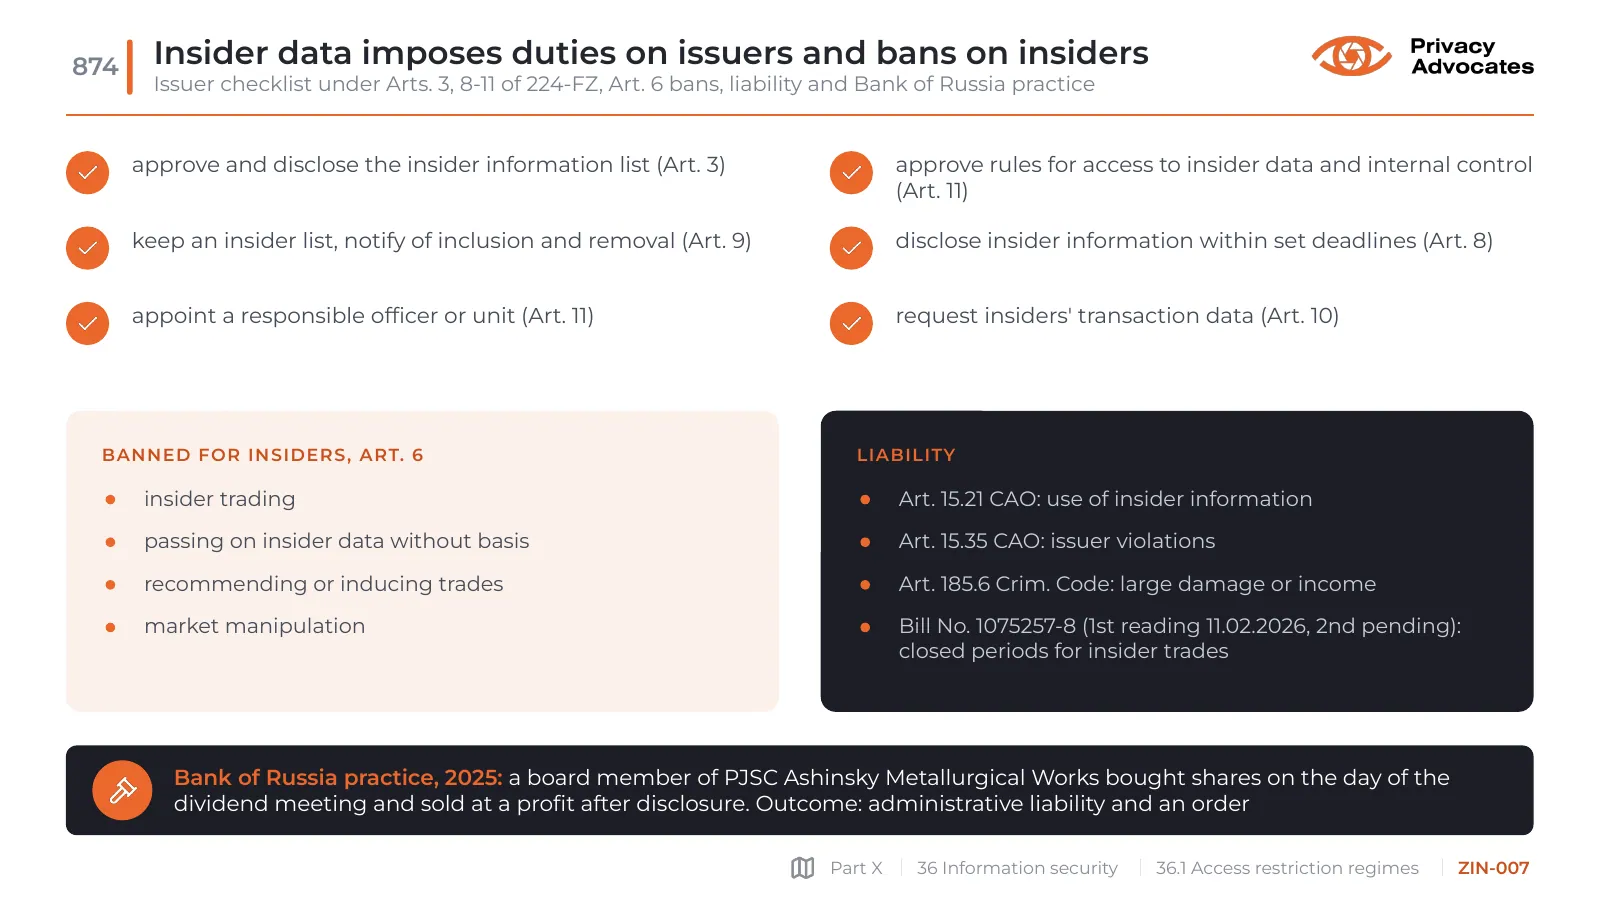
Insider data imposes duties on issuers and bans on insiders

Issuer checklist under Arts. 3, 8-11 of 224-FZ, Art. 6 bans, liability and Bank of Russia practice

Slide ZIN-007: Insider data imposes duties on issuers and bans on insiders
Slide text

approve and disclose the insider information list (Art. 3)

keep an insider list, notify of inclusion and removal (Art. 9)

appoint a responsible officer or unit (Art. 11)

approve rules for access to insider data and internal control (Art. 11)

disclose insider information within set deadlines (Art. 8)

request insiders' transaction data (Art. 10)

Banned for insiders, Art. 6

insider trading

passing on insider data without basis

recommending or inducing trades

market manipulation

Liability

Art. 15.21 CAO: use of insider information

Art. 15.35 CAO: issuer violations

Art. 185.6 Crim. Code: large damage or income

Bill No. 1075257-8 (1st reading 11.02.2026, 2nd pending): closed periods for insider trades

Bank of Russia practice, 2025: a board member of PJSC Ashinsky Metallurgical Works bought shares on the day of the dividend meeting and sold at a profit after disclosure. Outcome: administrative liability and an order

ZIN-008

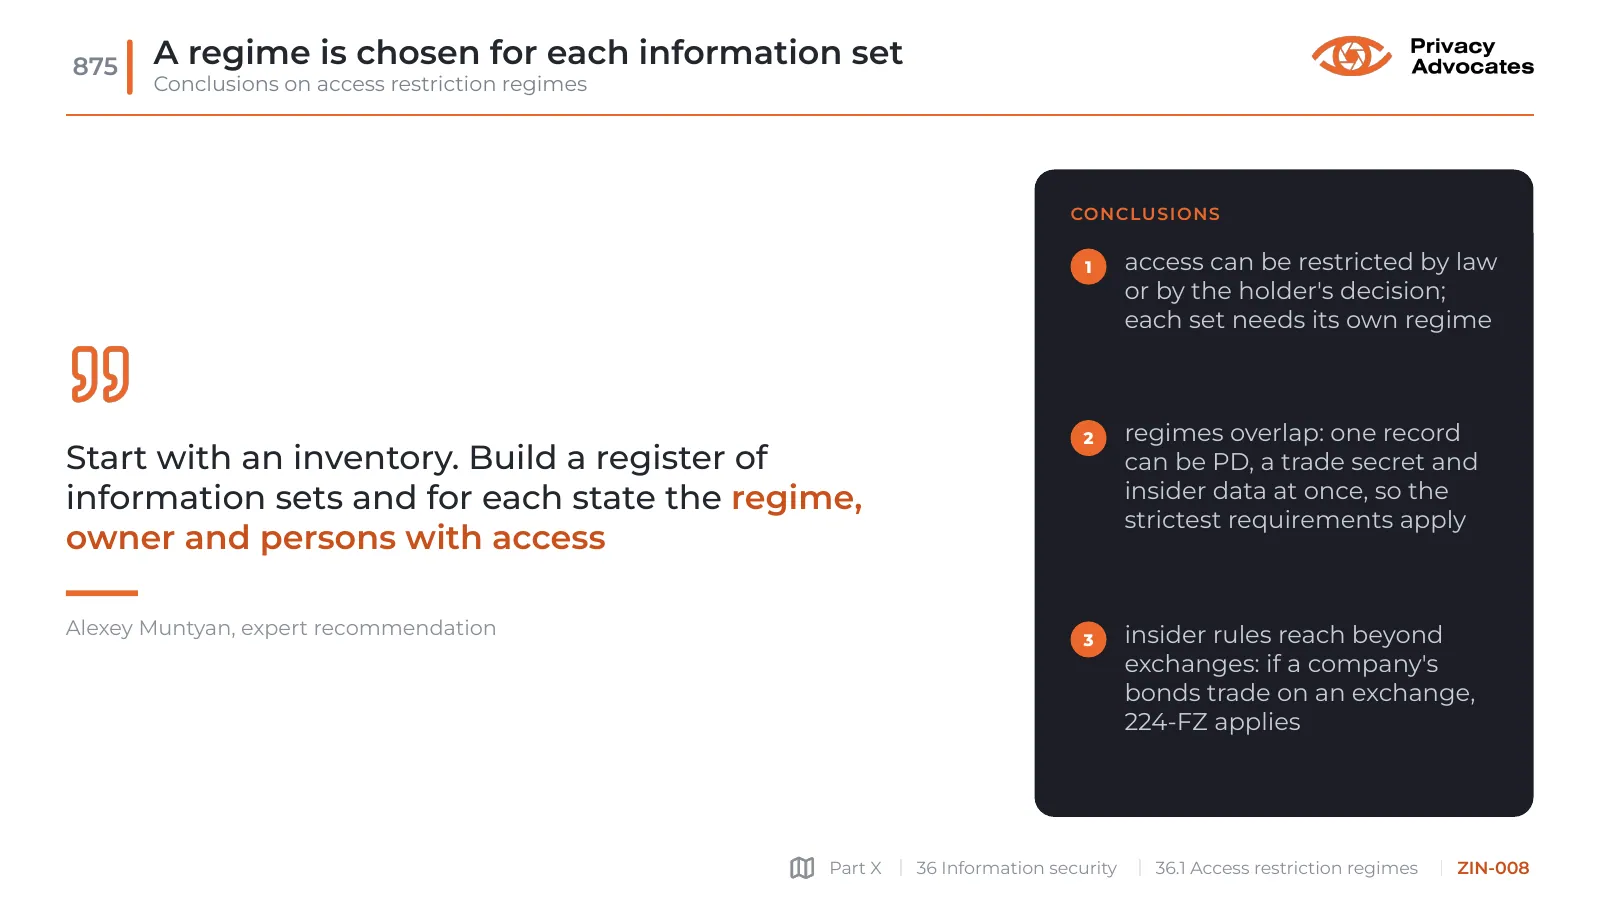
A regime is chosen for each information set

Conclusions on access restriction regimes

Slide ZIN-008: A regime is chosen for each information set
Slide text

Start with an inventory. Build a register of information sets and for each state the regime, owner and persons with access

Alexey Muntyan, expert recommendation

Conclusions

1

access can be restricted by law or by the holder's decision; each set needs its own regime

2

regimes overlap: one record can be PD, a trade secret and insider data at once, so the strictest requirements apply

3

insider rules reach beyond exchanges: if a company's bonds trade on an exchange, 224-FZ applies

36.2

Trade secrets and official information

Trade secret criteria and the measures the regime requires

ZIN-009

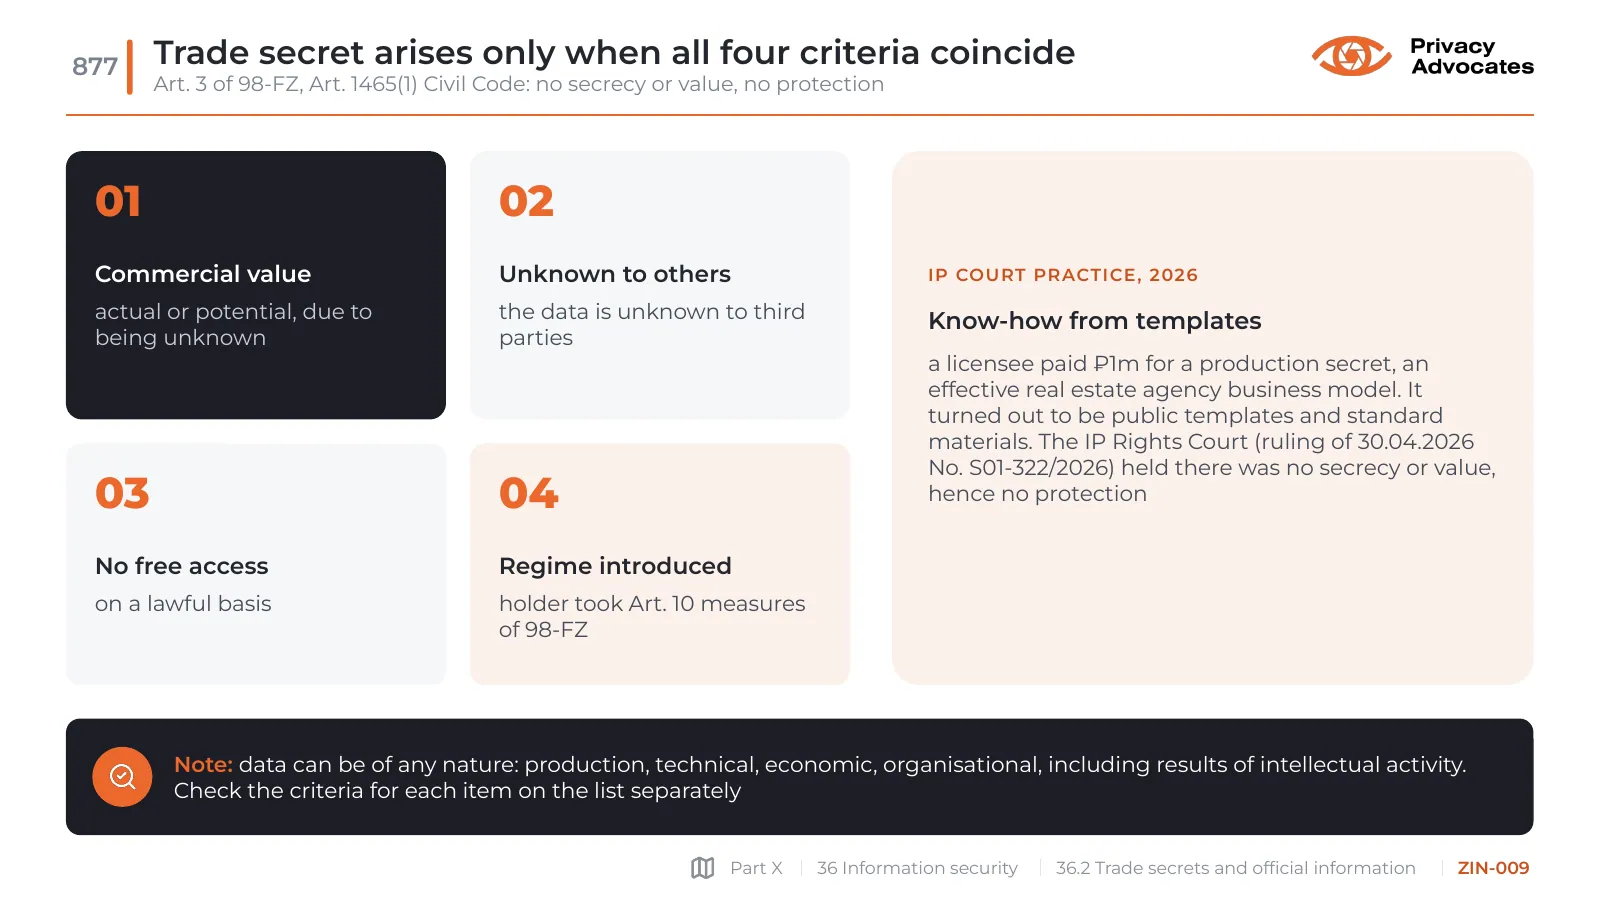
Trade secret arises only when all four criteria coincide

Art. 3 of 98-FZ, Art. 1465(1) Civil Code: no secrecy or value, no protection

Slide ZIN-009: Trade secret arises only when all four criteria coincide
Slide text

01

Commercial value

actual or potential, due to being unknown

02

Unknown to others

the data is unknown to third parties

03

No free access

on a lawful basis

04

Regime introduced

holder took Art. 10 measures of 98-FZ

IP Court practice, 2026

Know-how from templates

a licensee paid ₽1m for a production secret, an effective real estate agency business model. It turned out to be public templates and standard materials. The IP Rights Court (ruling of 30.04.2026 No. S01-322/2026) held there was no secrecy or value, hence no protection

Note: data can be of any nature: production, technical, economic, organisational, including results of intellectual activity. Check the criteria for each item on the list separately

ZIN-010

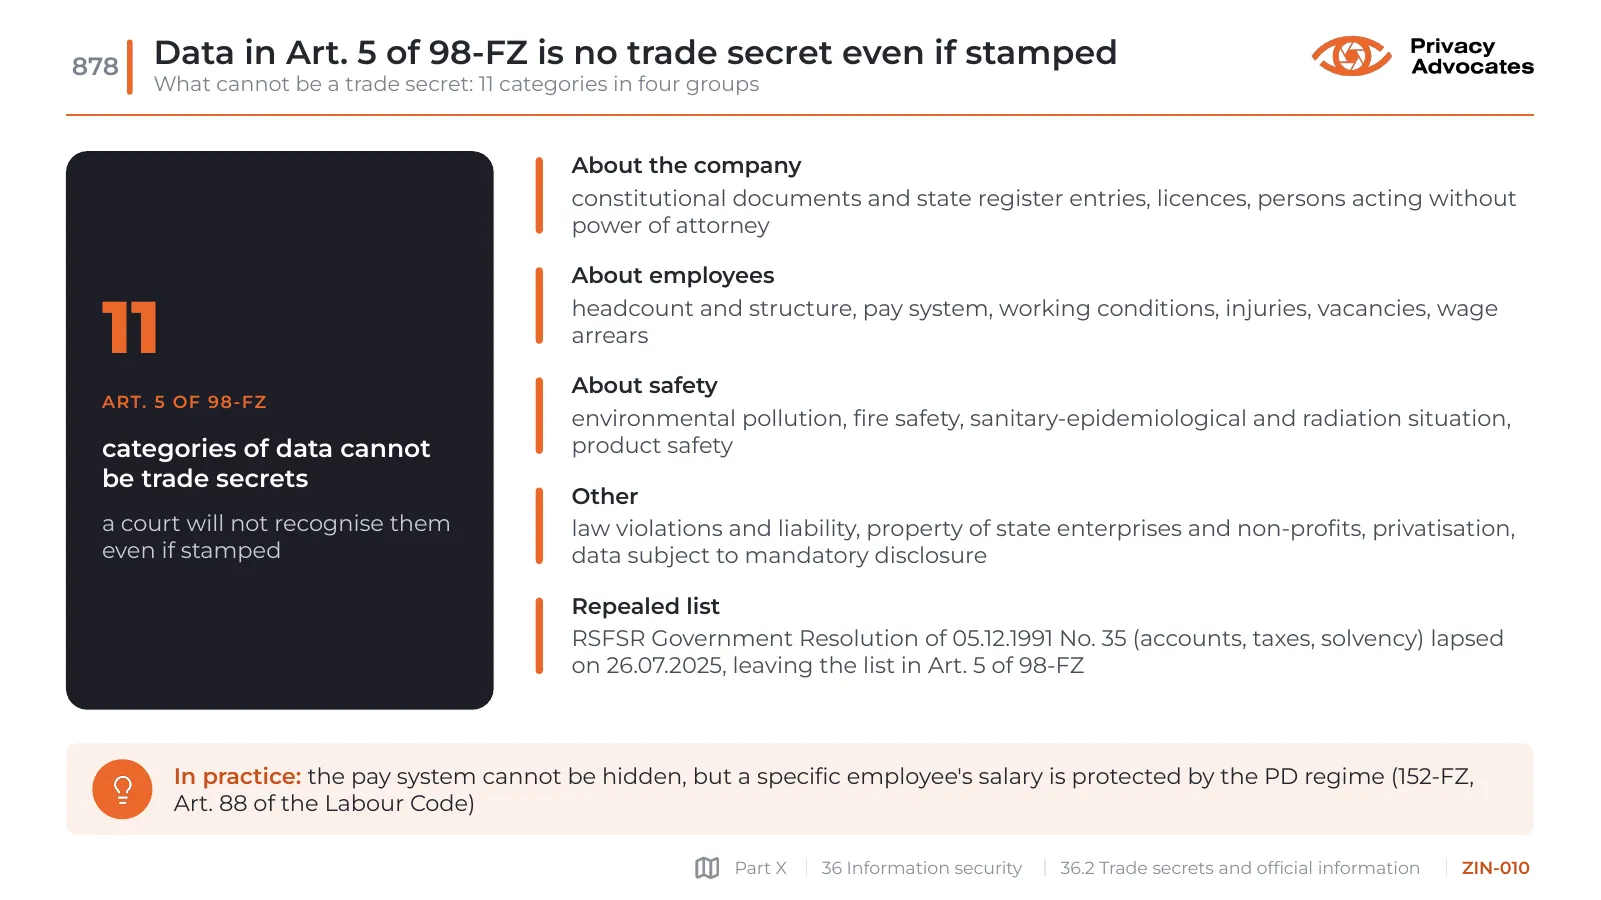
Data in Art. 5 of 98-FZ is no trade secret even if stamped

What cannot be a trade secret: 11 categories in four groups

Slide ZIN-010: Data in Art. 5 of 98-FZ is no trade secret even if stamped
Slide text

11

Art. 5 of 98-FZ

categories of data cannot be trade secrets

a court will not recognise them even if stamped

About the company

constitutional documents and state register entries, licences, persons acting without power of attorney

About employees

headcount and structure, pay system, working conditions, injuries, vacancies, wage arrears

About safety

environmental pollution, fire safety, sanitary-epidemiological and radiation situation, product safety

Other

law violations and liability, property of state enterprises and non-profits, privatisation, data subject to mandatory disclosure

Repealed list

RSFSR Government Resolution of 05.12.1991 No. 35 (accounts, taxes, solvency) lapsed on 26.07.2025, leaving the list in Art. 5 of 98-FZ

In practice: the pay system cannot be hidden, but a specific employee's salary is protected by the PD regime (152-FZ, Art. 88 of the Labour Code)

ZIN-011

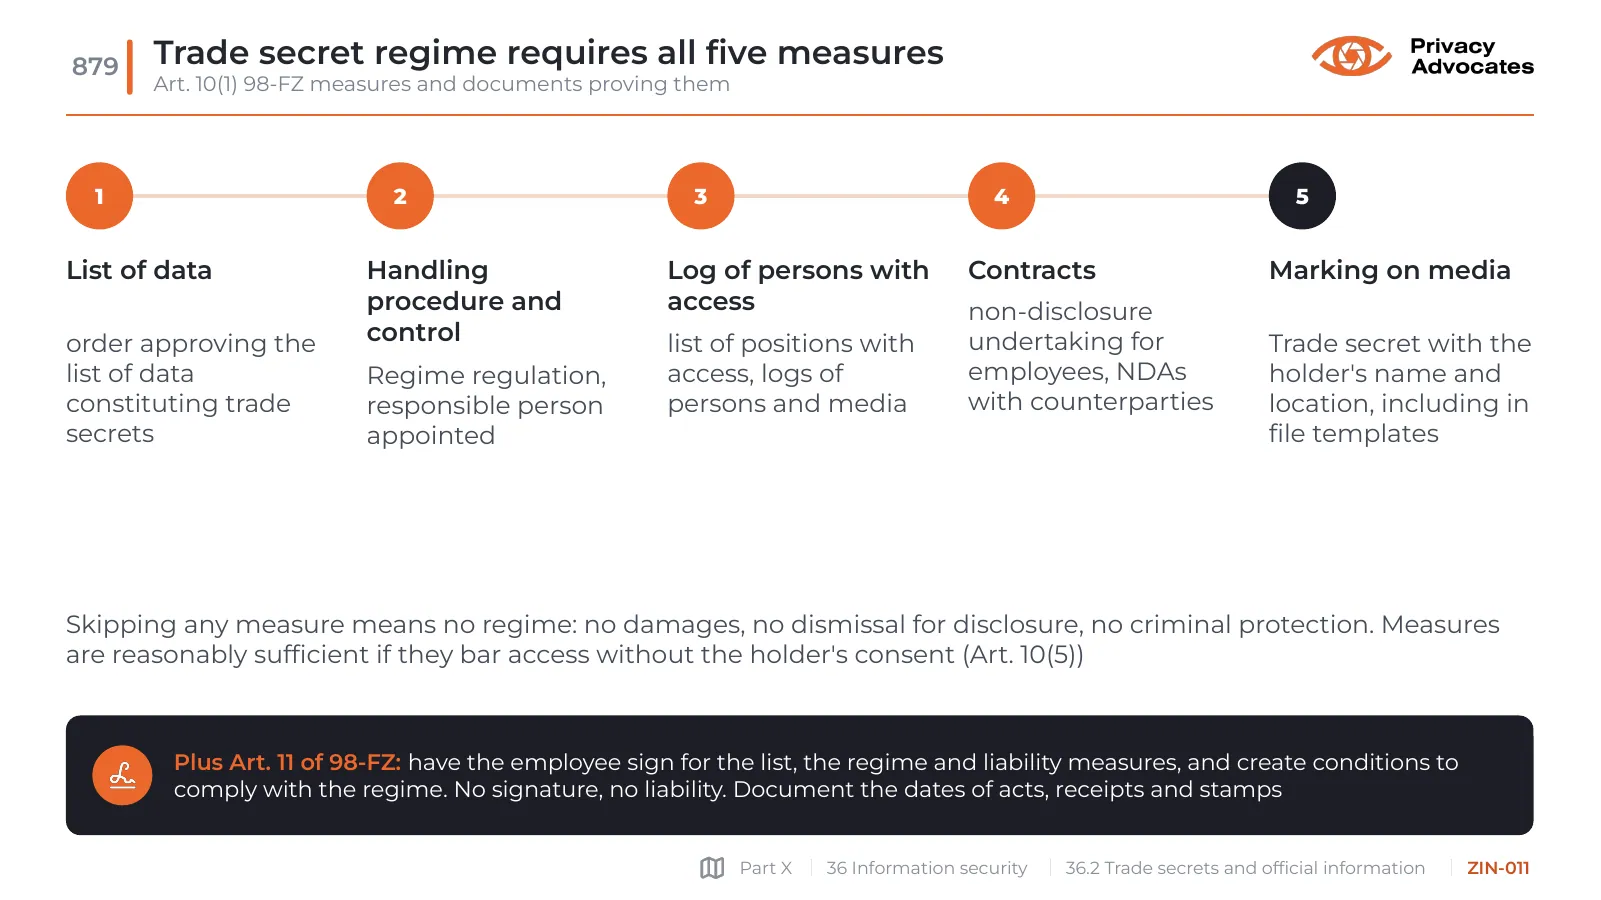
Trade secret regime requires all five measures

Art. 10(1) 98-FZ measures and documents proving them

Slide ZIN-011: Trade secret regime requires all five measures
Slide text

1

List of data

order approving the list of data constituting trade secrets

2

Handling procedure and control

Regime regulation, responsible person appointed

3

Log of persons with access

list of positions with access, logs of persons and media

4

Contracts

non-disclosure undertaking for employees, NDAs with counterparties

5

Marking on media

Trade secret with the holder's name and location, including in file templates

Skipping any measure means no regime: no damages, no dismissal for disclosure, no criminal protection. Measures are reasonably sufficient if they bar access without the holder's consent (Art. 10(5))

Plus Art. 11 of 98-FZ: have the employee sign for the list, the regime and liability measures, and create conditions to comply with the regime. No signature, no liability. Document the dates of acts, receipts and stamps

ZIN-012

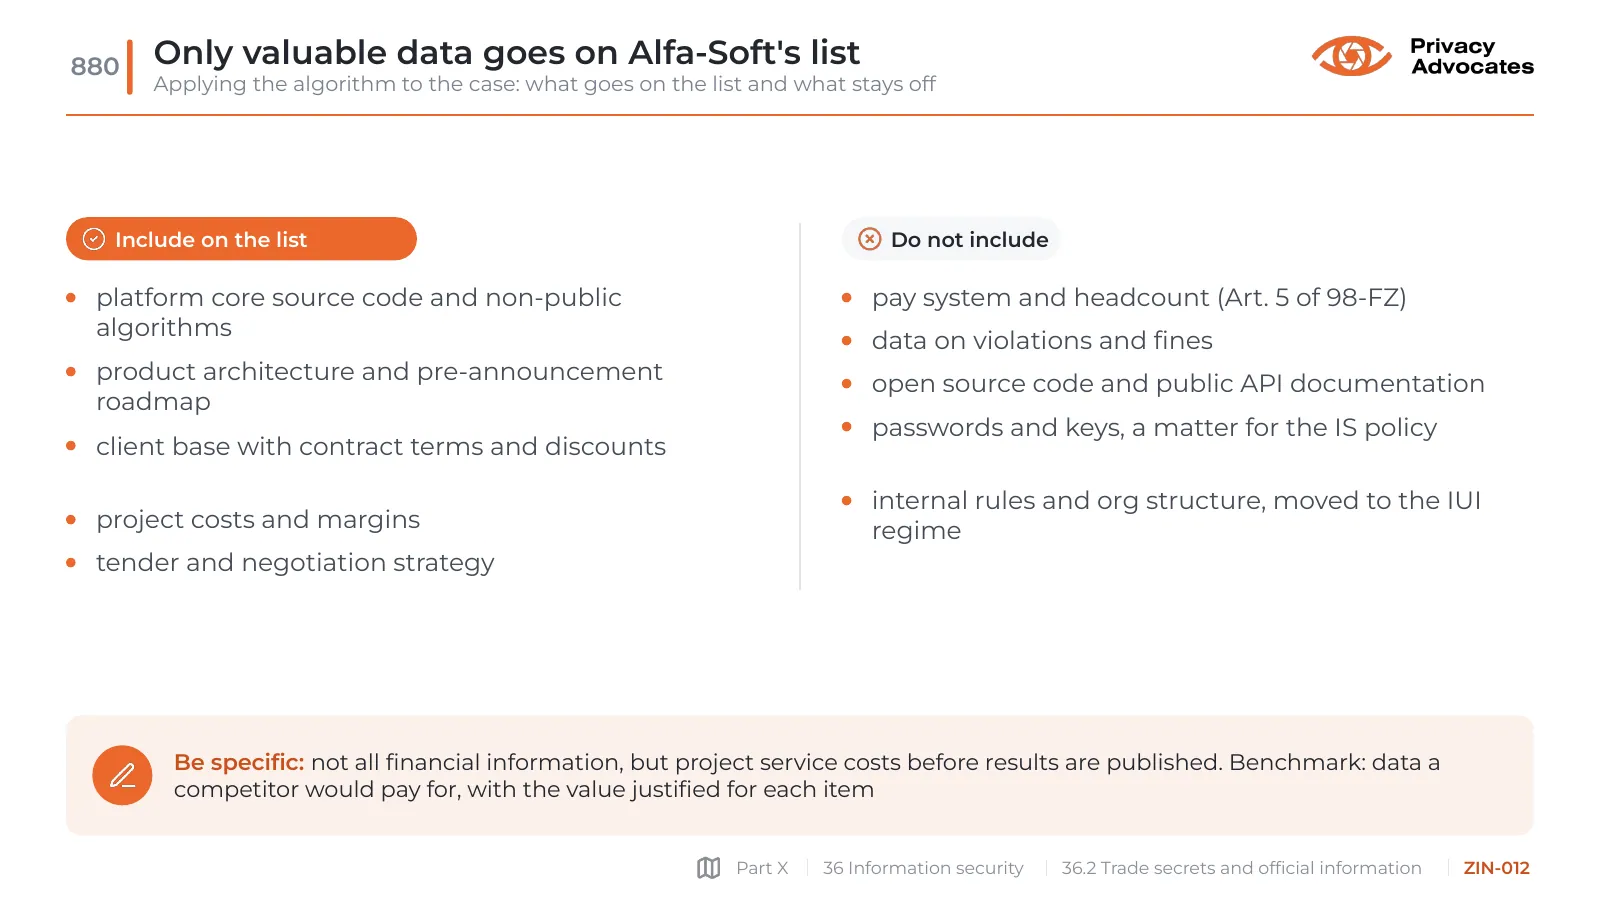
Only valuable data goes on Alfa-Soft's list

Applying the algorithm to the case: what goes on the list and what stays off

Slide ZIN-012: Only valuable data goes on Alfa-Soft's list
Slide text

Include on the list

platform core source code and non-public algorithms

product architecture and pre-announcement roadmap

client base with contract terms and discounts

project costs and margins

tender and negotiation strategy

Do not include

pay system and headcount (Art. 5 of 98-FZ)

data on violations and fines

open source code and public API documentation

passwords and keys, a matter for the IS policy

internal rules and org structure, moved to the IUI regime

Be specific: not all financial information, but project service costs before results are published. Benchmark: data a competitor would pay for, with the value justified for each item

ZIN-013

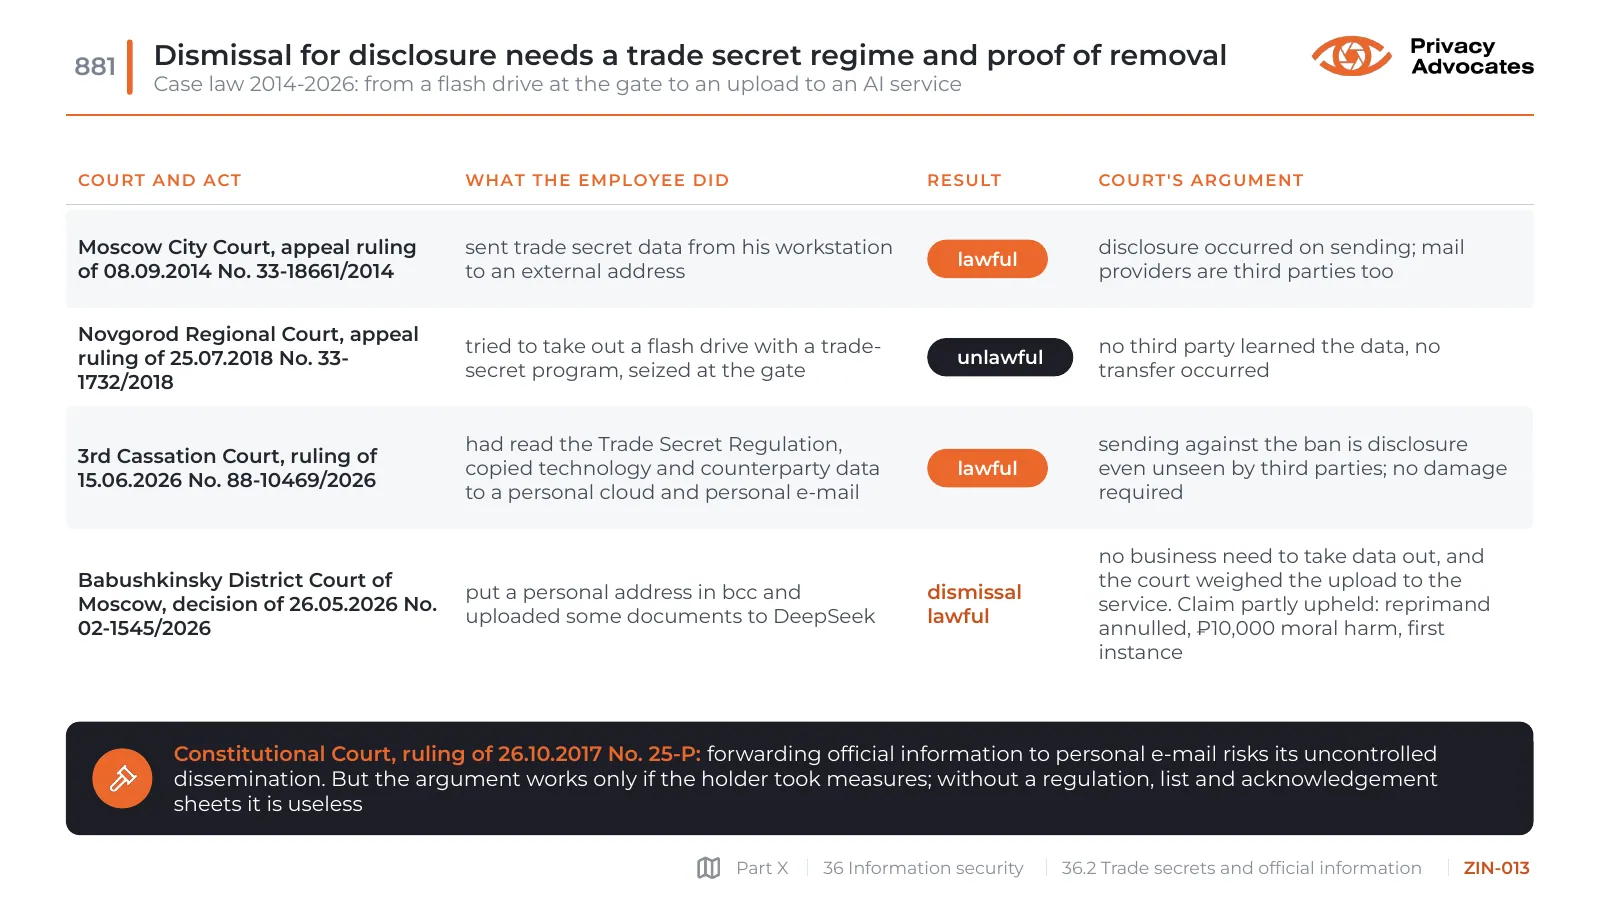
Dismissal for disclosure needs a trade secret regime and proof of removal

Case law 2014-2026: from a flash drive at the gate to an upload to an AI service

Slide ZIN-013: Dismissal for disclosure needs a trade secret regime and proof of removal
Slide text
  • Court and act
  • What the employee did
  • Result
  • Court's argument
  • Moscow City Court, appeal ruling of 08.09.2014 No. 33-18661/2014
  • sent trade secret data from his workstation to an external address
  • lawful
  • disclosure occurred on sending; mail providers are third parties too
  • Novgorod Regional Court, appeal ruling of 25.07.2018 No. 33-1732/2018
  • tried to take out a flash drive with a trade-secret program, seized at the gate
  • unlawful
  • no third party learned the data, no transfer occurred
  • 3rd Cassation Court, ruling of 15.06.2026 No. 88-10469/2026
  • had read the Trade Secret Regulation, copied technology and counterparty data to a personal cloud and personal e-mail
  • lawful
  • sending against the ban is disclosure even unseen by third parties; no damage required
  • Babushkinsky District Court of Moscow, decision of 26.05.2026 No. 02-1545/2026
  • put a personal address in bcc and uploaded some documents to DeepSeek
  • dismissal lawful
  • no business need to take data out, and the court weighed the upload to the service. Claim partly upheld: reprimand annulled, ₽10,000 moral harm, first instance

Constitutional Court, ruling of 26.10.2017 No. 25-P: forwarding official information to personal e-mail risks its uncontrolled dissemination. But the argument works only if the holder took measures; without a regulation, list and acknowledgement sheets it is useless

ZIN-014

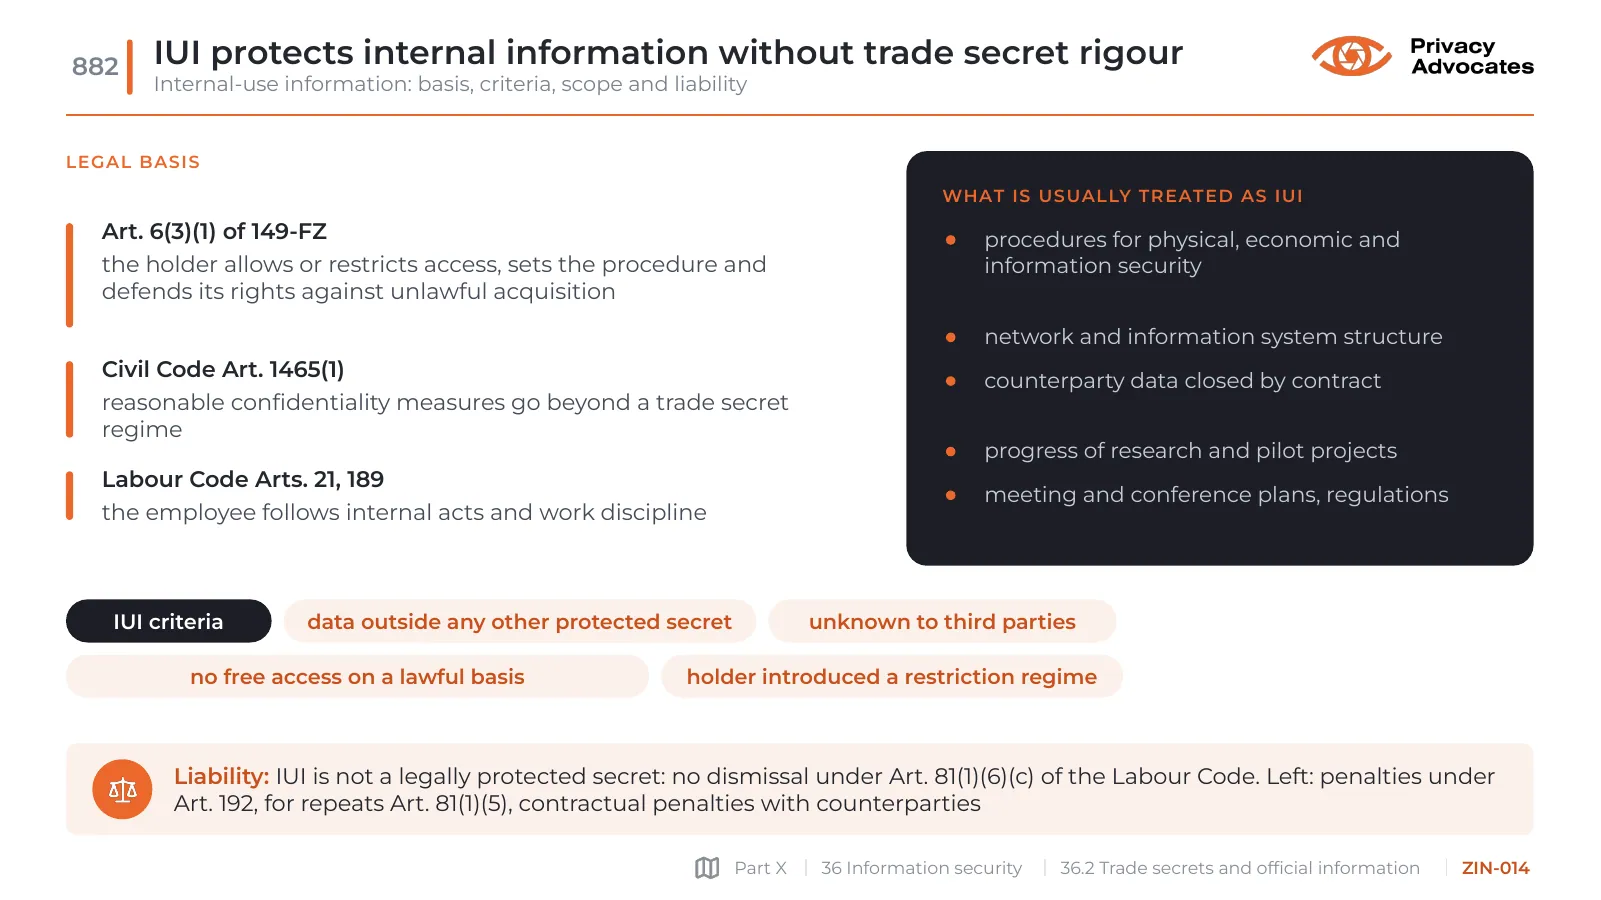
IUI protects internal information without trade secret rigour

Internal-use information: basis, criteria, scope and liability

Slide ZIN-014: IUI protects internal information without trade secret rigour
Slide text

Legal basis

Art. 6(3)(1) of 149-FZ

the holder allows or restricts access, sets the procedure and defends its rights against unlawful acquisition

Civil Code Art. 1465(1)

reasonable confidentiality measures go beyond a trade secret regime

Labour Code Arts. 21, 189

the employee follows internal acts and work discipline

What is usually treated as IUI

procedures for physical, economic and information security

network and information system structure

counterparty data closed by contract

progress of research and pilot projects

meeting and conference plans, regulations

  • IUI criteria
  • data outside any other protected secret
  • unknown to third parties
  • no free access on a lawful basis
  • holder introduced a restriction regime

Liability: IUI is not a legally protected secret: no dismissal under Art. 81(1)(6)(c) of the Labour Code. Left: penalties under Art. 192, for repeats Art. 81(1)(5), contractual penalties with counterparties

ZIN-015

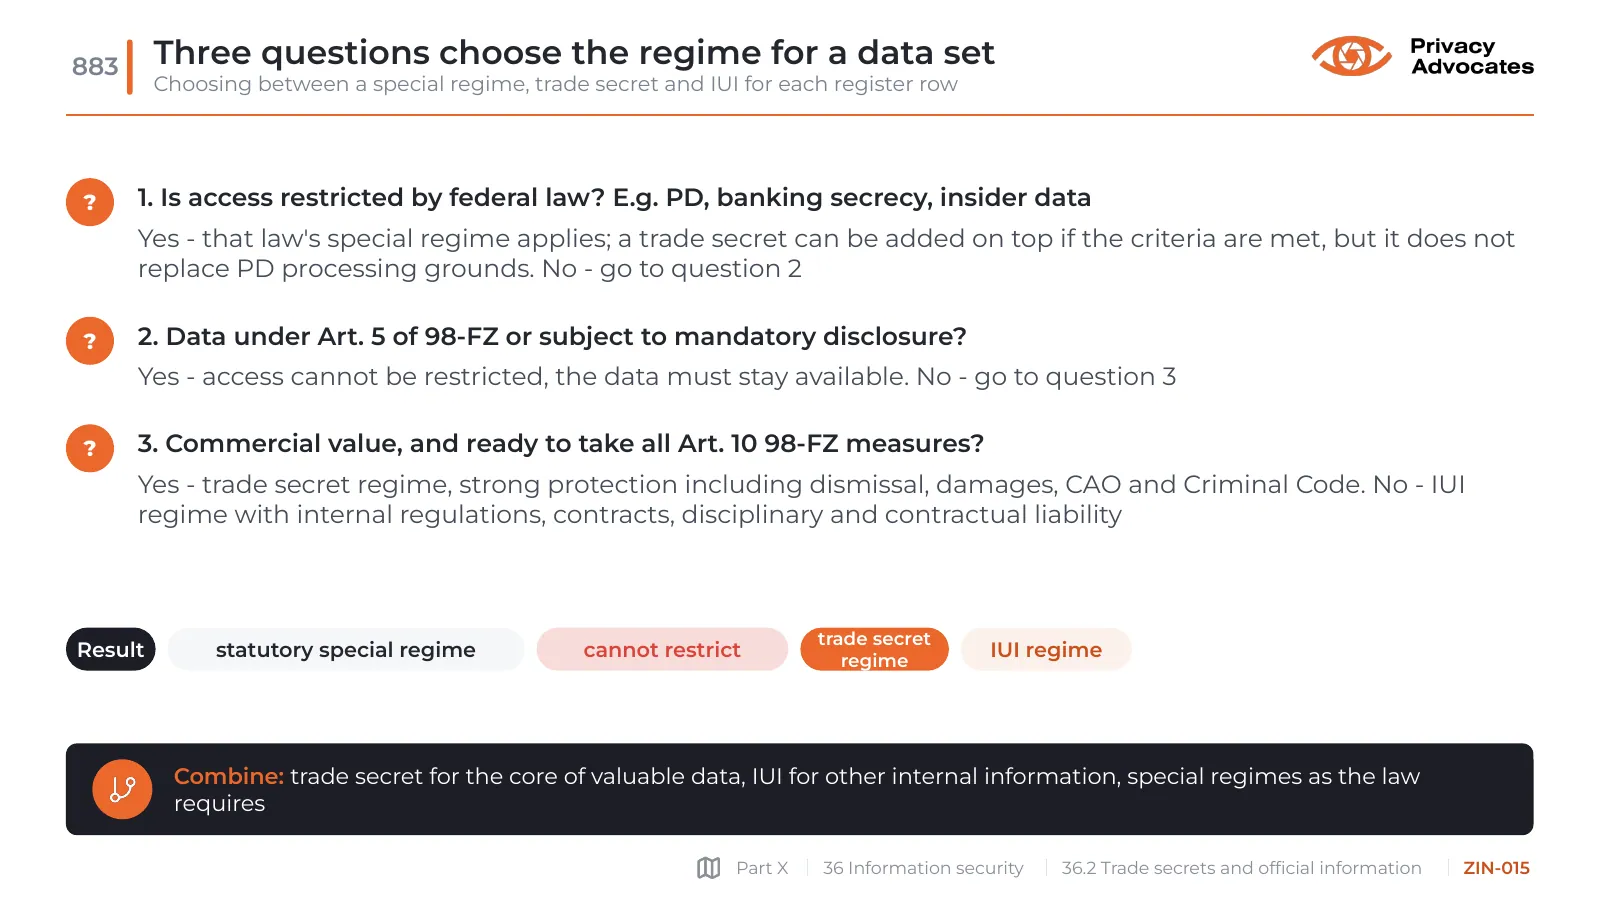
Three questions choose the regime for a data set

Choosing between a special regime, trade secret and IUI for each register row

Slide ZIN-015: Three questions choose the regime for a data set
Slide text
  • ?
  • 1. Is access restricted by federal law? E.g. PD, banking secrecy, insider data

Yes - that law's special regime applies; a trade secret can be added on top if the criteria are met, but it does not replace PD processing grounds. No - go to question 2

  • ?
  • 2. Data under Art. 5 of 98-FZ or subject to mandatory disclosure?

Yes - access cannot be restricted, the data must stay available. No - go to question 3

  • ?
  • 3. Commercial value, and ready to take all Art. 10 98-FZ measures?

Yes - trade secret regime, strong protection including dismissal, damages, CAO and Criminal Code. No - IUI regime with internal regulations, contracts, disciplinary and contractual liability

  • Result
  • statutory special regime
  • cannot restrict
  • trade secret regime
  • IUI regime

Combine: trade secret for the core of valuable data, IUI for other internal information, special regimes as the law requires

ZIN-016

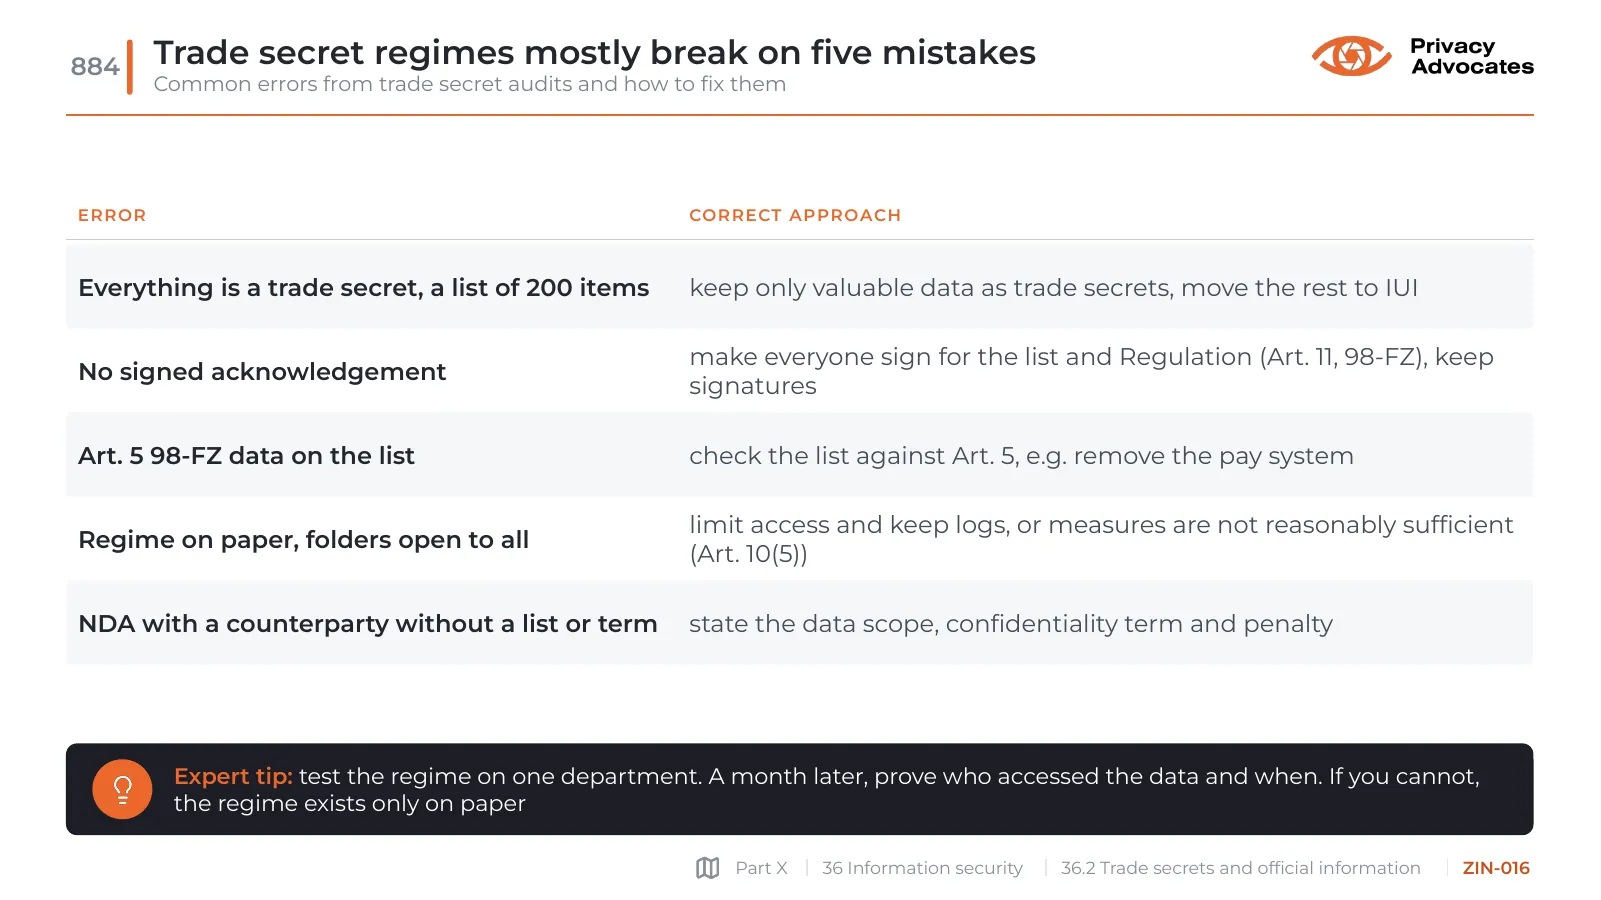
Trade secret regimes mostly break on five mistakes

Common errors from trade secret audits and how to fix them

Slide ZIN-016: Trade secret regimes mostly break on five mistakes
Slide text
  • Error
  • Correct approach
  • Everything is a trade secret, a list of 200 items
  • keep only valuable data as trade secrets, move the rest to IUI
  • No signed acknowledgement
  • make everyone sign for the list and Regulation (Art. 11, 98-FZ), keep signatures
  • Art. 5 98-FZ data on the list
  • check the list against Art. 5, e.g. remove the pay system
  • Regime on paper, folders open to all
  • limit access and keep logs, or measures are not reasonably sufficient (Art. 10(5))
  • NDA with a counterparty without a list or term
  • state the data scope, confidentiality term and penalty

Expert tip: test the regime on one department. A month later, prove who accessed the data and when. If you cannot, the regime exists only on paper

ZIN-017

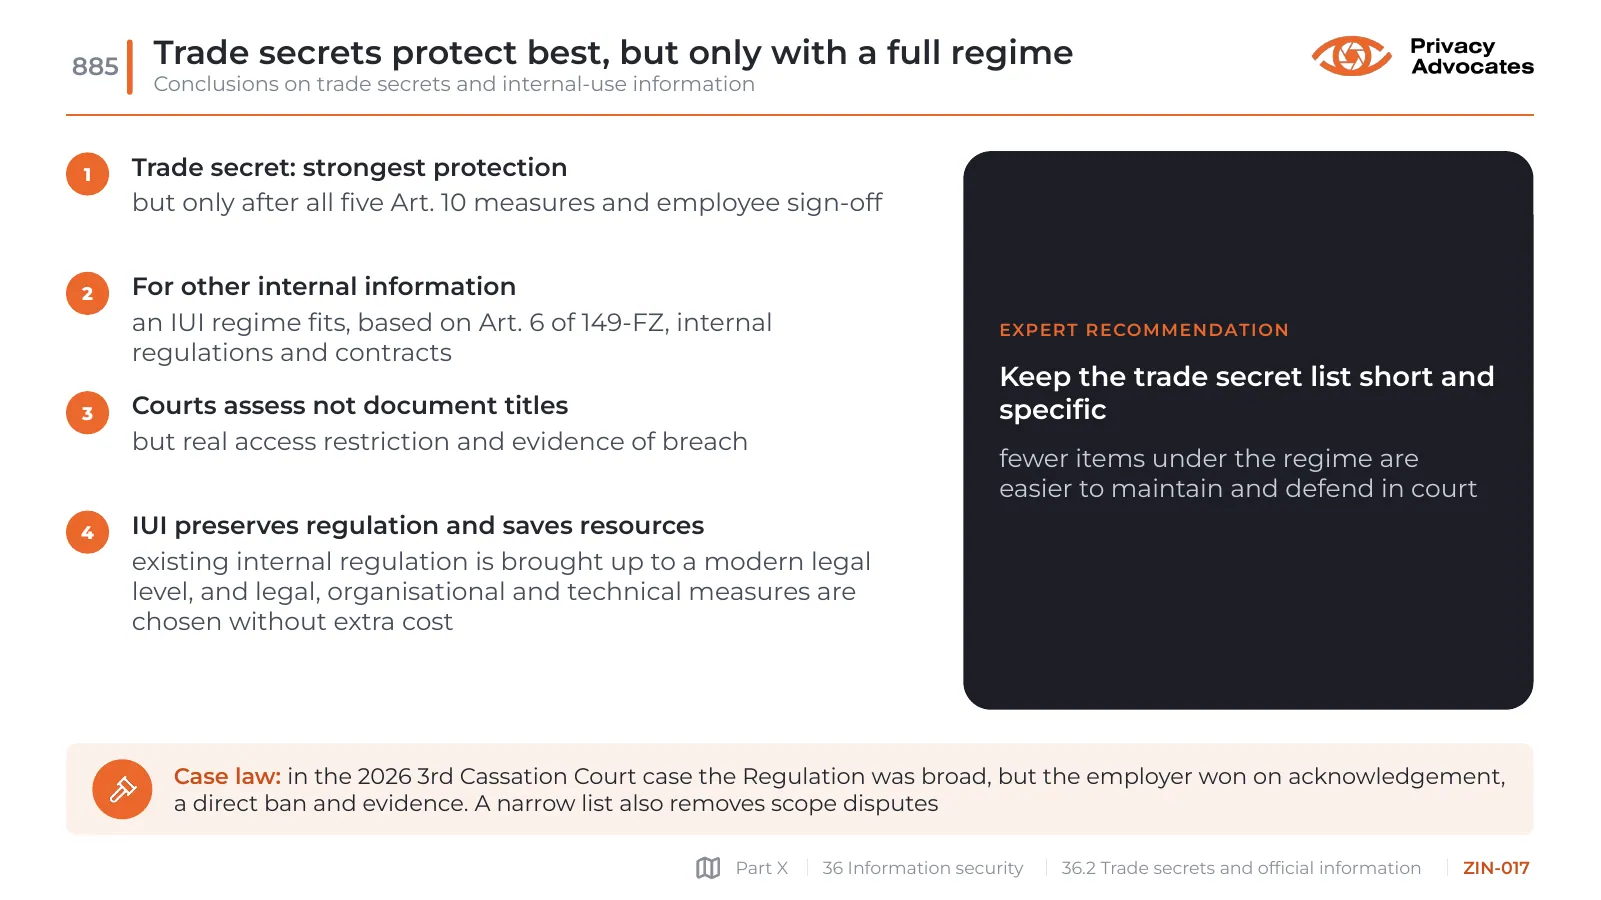
Trade secrets protect best, but only with a full regime

Conclusions on trade secrets and internal-use information

Slide ZIN-017: Trade secrets protect best, but only with a full regime
Slide text
  • 1
  • Trade secret: strongest protection

but only after all five Art. 10 measures and employee sign-off

  • 2
  • For other internal information

an IUI regime fits, based on Art. 6 of 149-FZ, internal regulations and contracts

  • 3
  • Courts assess not document titles

but real access restriction and evidence of breach

  • 4
  • IUI preserves regulation and saves resources

existing internal regulation is brought up to a modern legal level, and legal, organisational and technical measures are chosen without extra cost

Expert recommendation

Keep the trade secret list short and specific

fewer items under the regime are easier to maintain and defend in court

Case law: in the 2026 3rd Cassation Court case the Regulation was broad, but the employer won on acknowledgement, a direct ban and evidence. A narrow list also removes scope disputes

36.3

Information security management system

How the legal regime relates to infosec and how to build the system

ZIN-018

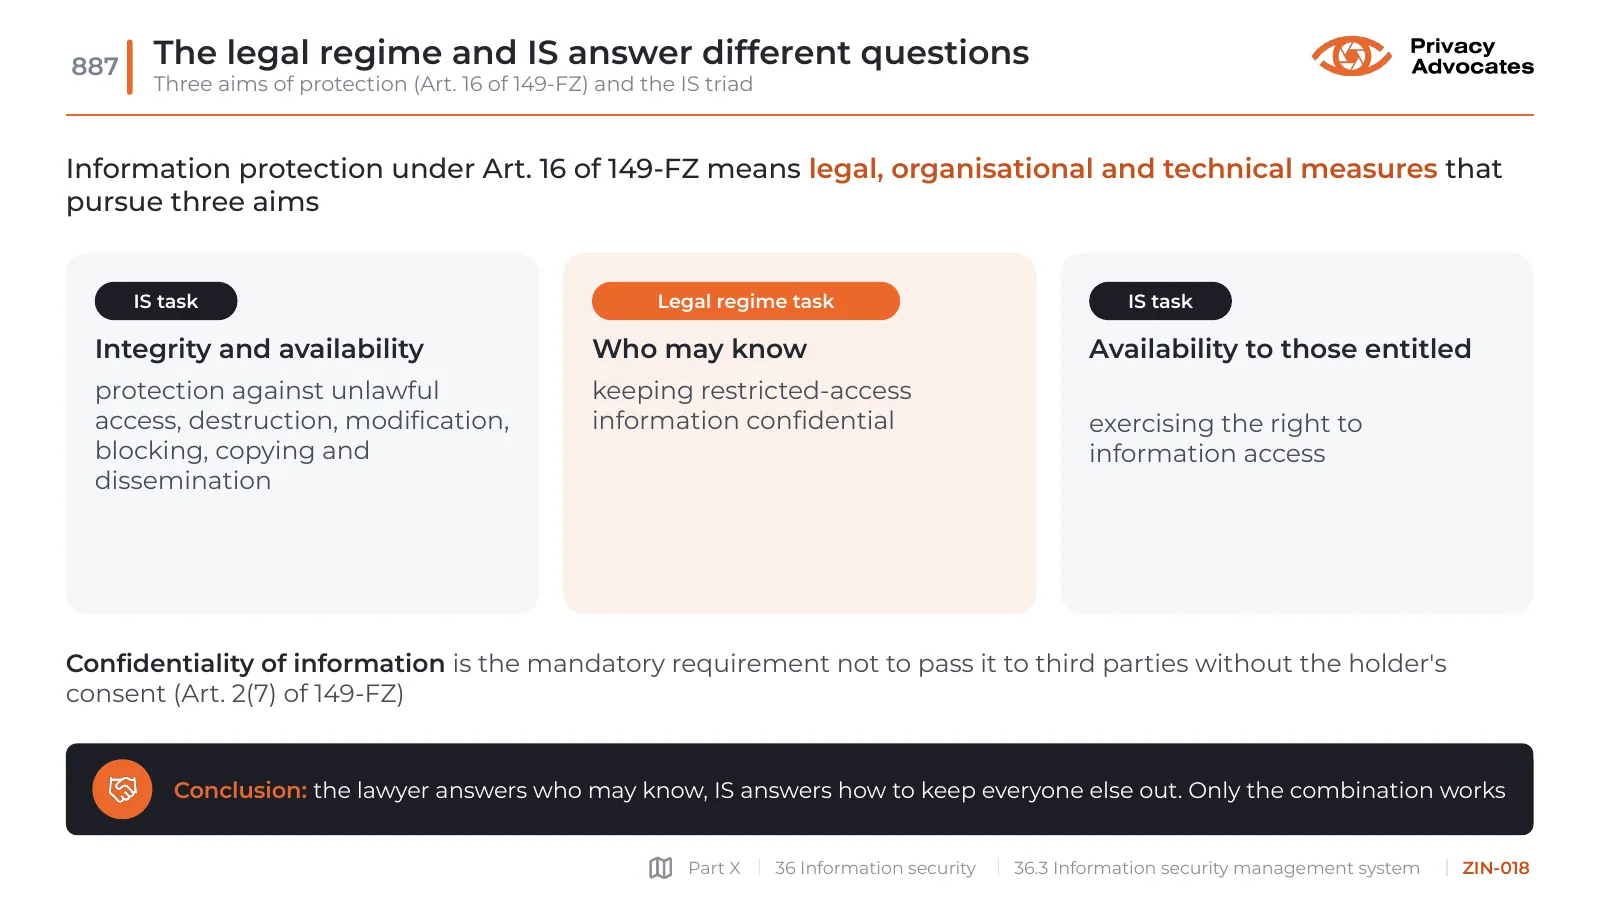
The legal regime and IS answer different questions

Three aims of protection (Art. 16 of 149-FZ) and the IS triad

Slide ZIN-018: The legal regime and IS answer different questions
Slide text

Information protection under Art. 16 of 149-FZ means legal, organisational and technical measures that pursue three aims

IS task

Integrity and availability

protection against unlawful access, destruction, modification, blocking, copying and dissemination

Legal regime task

Who may know

keeping restricted-access information confidential

IS task

Availability to those entitled

exercising the right to information access

Confidentiality of information is the mandatory requirement not to pass it to third parties without the holder's consent (Art. 2(7) of 149-FZ)

Conclusion: the lawyer answers who may know, IS answers how to keep everyone else out. Only the combination works

ZIN-019

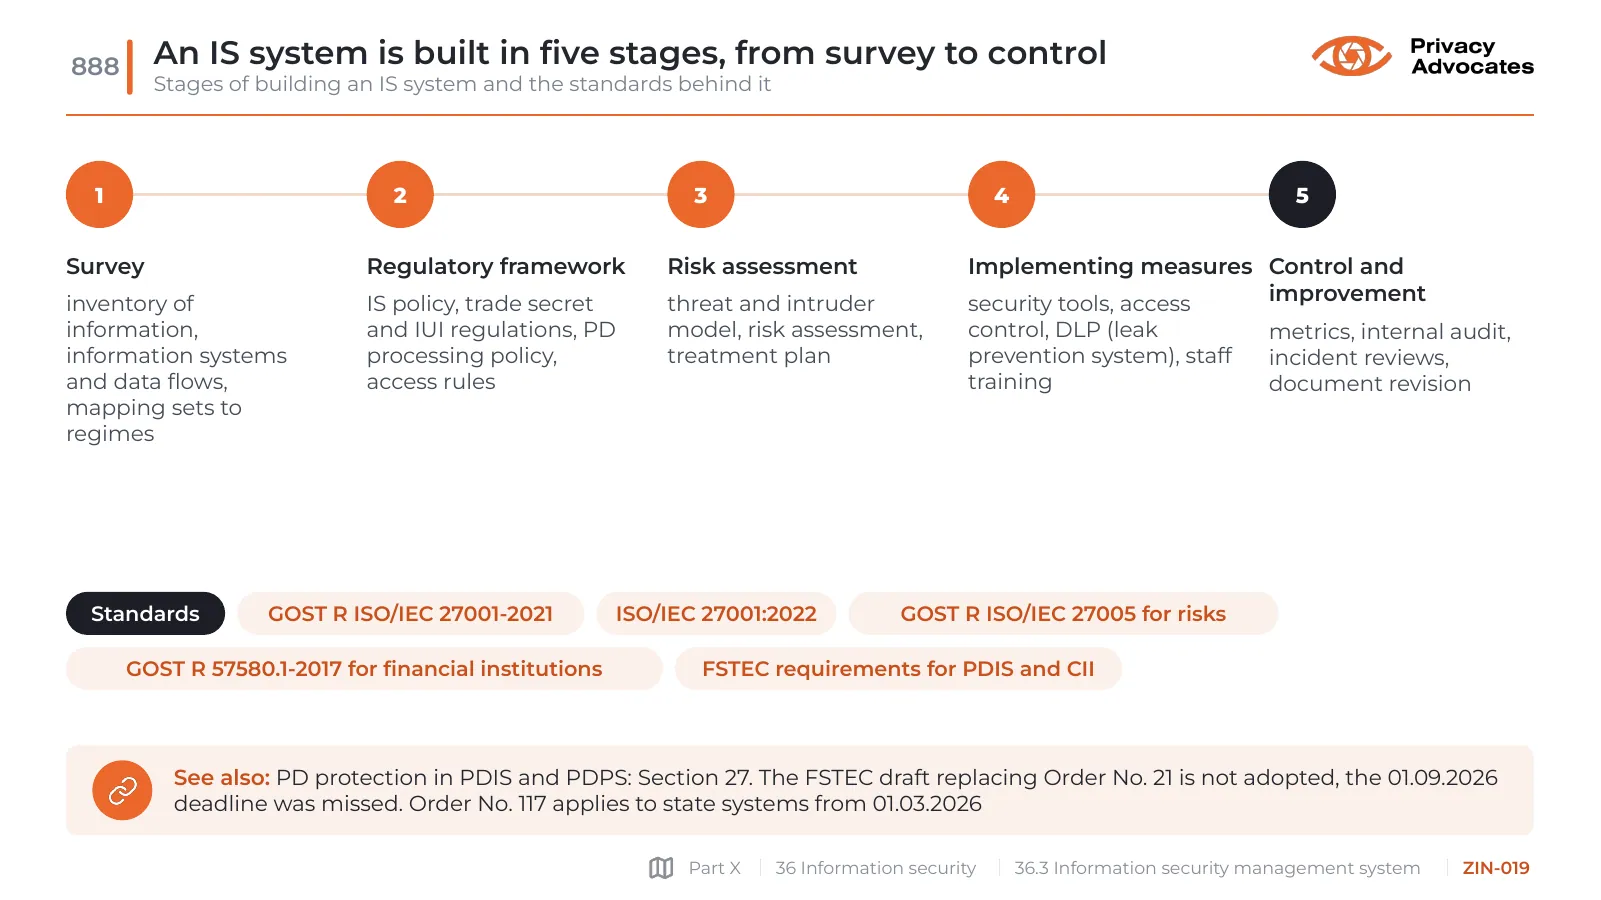
An IS system is built in five stages, from survey to control

Stages of building an IS system and the standards behind it

Slide ZIN-019: An IS system is built in five stages, from survey to control
Slide text

1

Survey

inventory of information, information systems and data flows, mapping sets to regimes

2

Regulatory framework

IS policy, trade secret and IUI regulations, PD processing policy, access rules

3

Risk assessment

threat and intruder model, risk assessment, treatment plan

4

Implementing measures

security tools, access control, DLP (leak prevention system), staff training

5

Control and improvement

metrics, internal audit, incident reviews, document revision

  • Standards
  • GOST R ISO/IEC 27001-2021
  • ISO/IEC 27001:2022
  • GOST R ISO/IEC 27005 for risks
  • GOST R 57580.1-2017 for financial institutions
  • FSTEC requirements for PDIS and CII

See also: PD protection in PDIS and PDPS: Section 27. The FSTEC draft replacing Order No. 21 is not adopted, the 01.09.2026 deadline was missed. Order No. 117 applies to state systems from 01.03.2026

ZIN-020

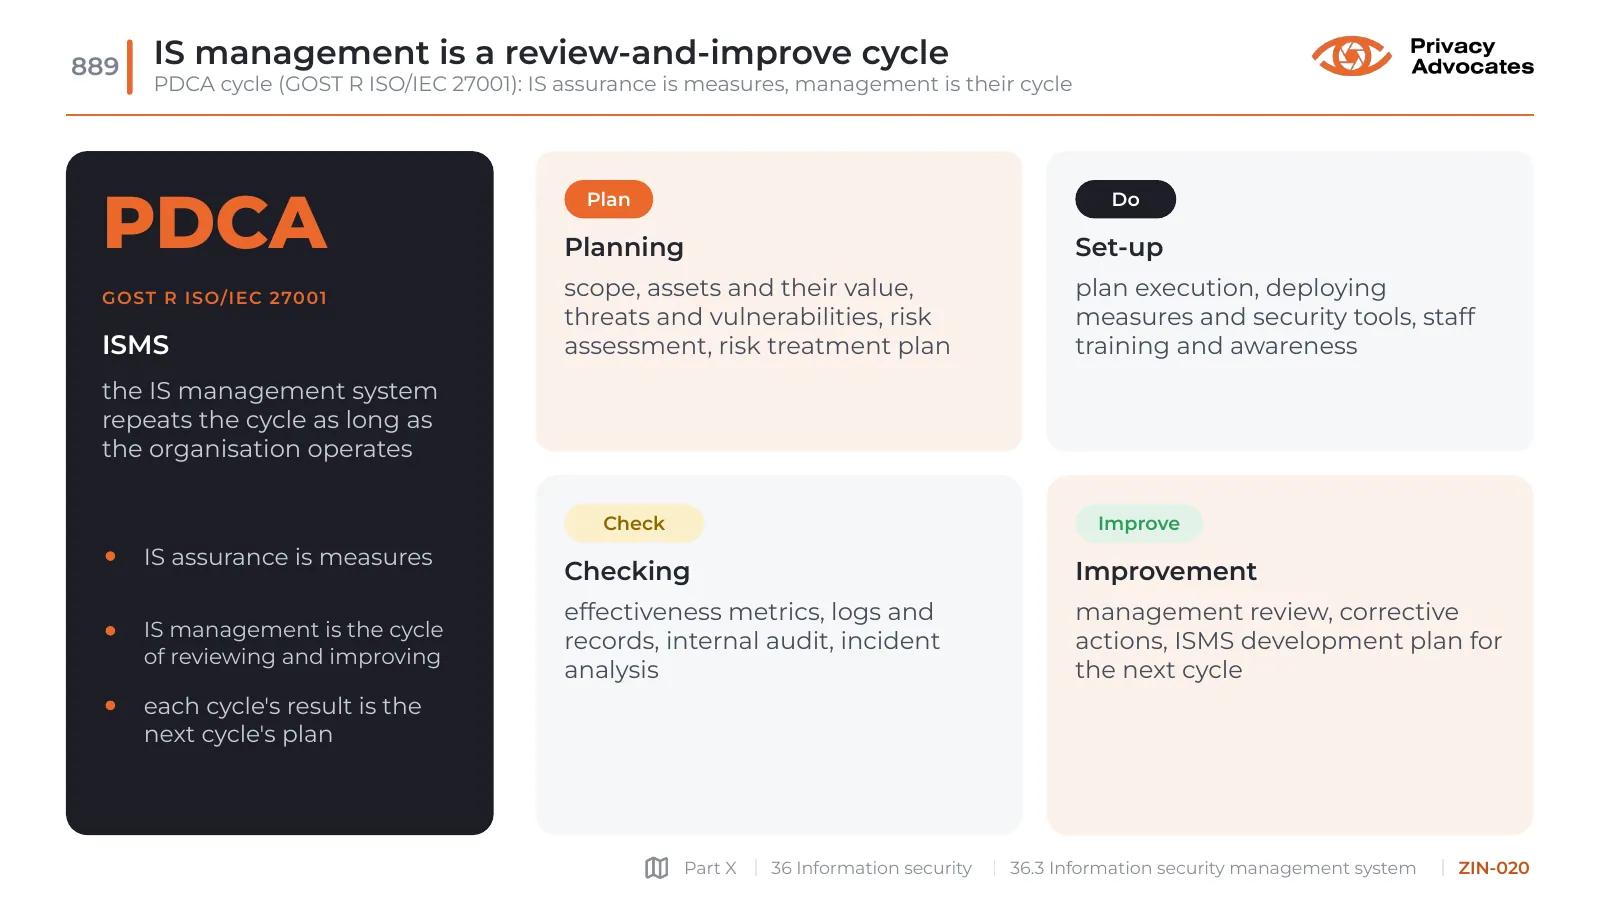
IS management is a review-and-improve cycle

PDCA cycle (GOST R ISO/IEC 27001): IS assurance is measures, management is their cycle

Slide ZIN-020: IS management is a review-and-improve cycle
Slide text

PDCA

GOST R ISO/IEC 27001

ISMS

the IS management system repeats the cycle as long as the organisation operates

IS assurance is measures

IS management is the cycle of reviewing and improving

each cycle's result is the next cycle's plan

Plan

Planning

scope, assets and their value, threats and vulnerabilities, risk assessment, risk treatment plan

Do

Set-up

plan execution, deploying measures and security tools, staff training and awareness

Check

Checking

effectiveness metrics, logs and records, internal audit, incident analysis

Improve

Improvement

management review, corrective actions, ISMS development plan for the next cycle

ZIN-021

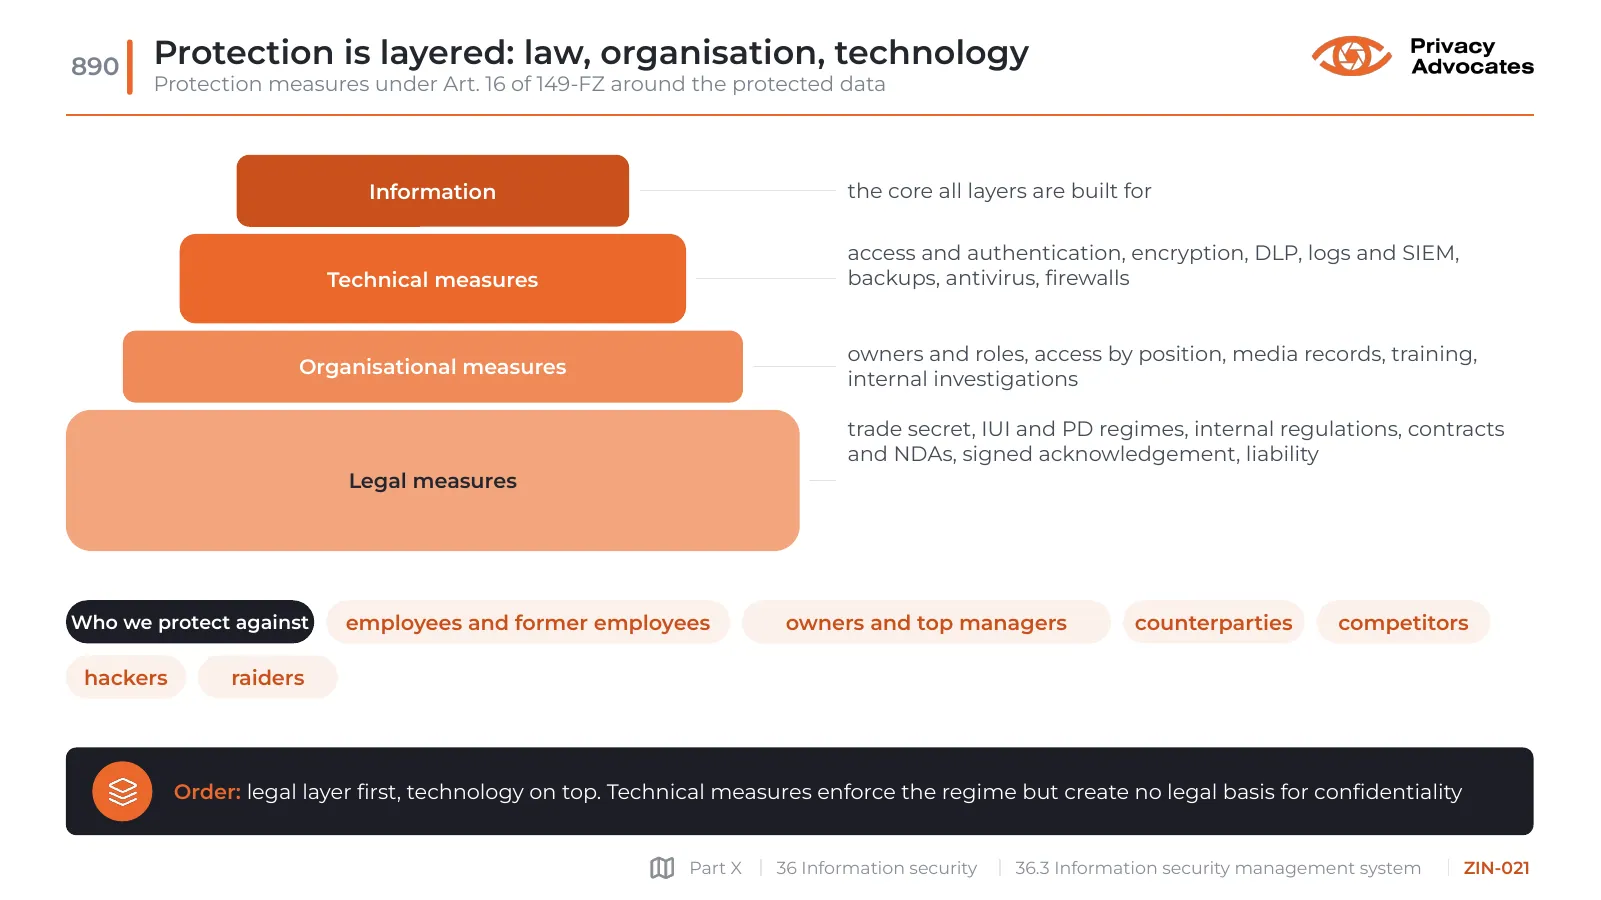
Protection is layered: law, organisation, technology

Protection measures under Art. 16 of 149-FZ around the protected data

Slide ZIN-021: Protection is layered: law, organisation, technology
Slide text
  • Information
  • the core all layers are built for
  • Technical measures
  • access and authentication, encryption, DLP, logs and SIEM, backups, antivirus, firewalls
  • Organisational measures
  • owners and roles, access by position, media records, training, internal investigations
  • Legal measures
  • trade secret, IUI and PD regimes, internal regulations, contracts and NDAs, signed acknowledgement, liability
  • Who we protect against
  • employees and former employees
  • owners and top managers
  • counterparties
  • competitors
  • hackers
  • raiders

Order: legal layer first, technology on top. Technical measures enforce the regime but create no legal basis for confidentiality

ZIN-022

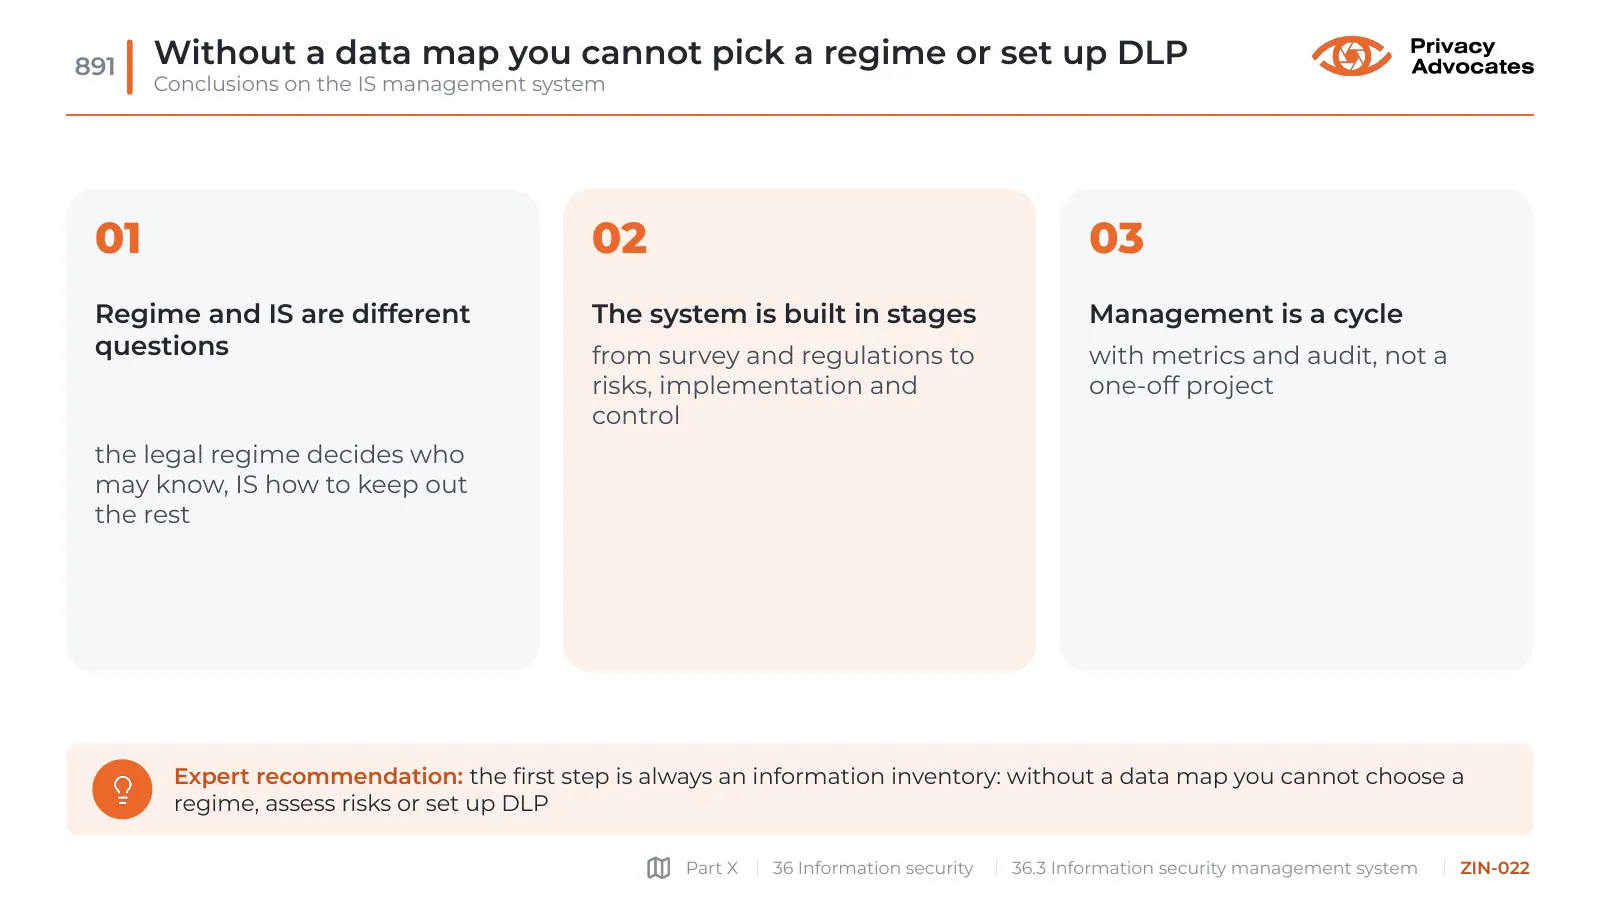
Without a data map you cannot pick a regime or set up DLP

Conclusions on the IS management system

Slide ZIN-022: Without a data map you cannot pick a regime or set up DLP
Slide text

01

Regime and IS are different questions

the legal regime decides who may know, IS how to keep out the rest

02

The system is built in stages

from survey and regulations to risks, implementation and control

03

Management is a cycle

with metrics and audit, not a one-off project

Expert recommendation: the first step is always an information inventory: without a data map you cannot choose a regime, assess risks or set up DLP

36.4

Staff monitoring and DLP

Limits of employee monitoring and legalising DLP

ZIN-023

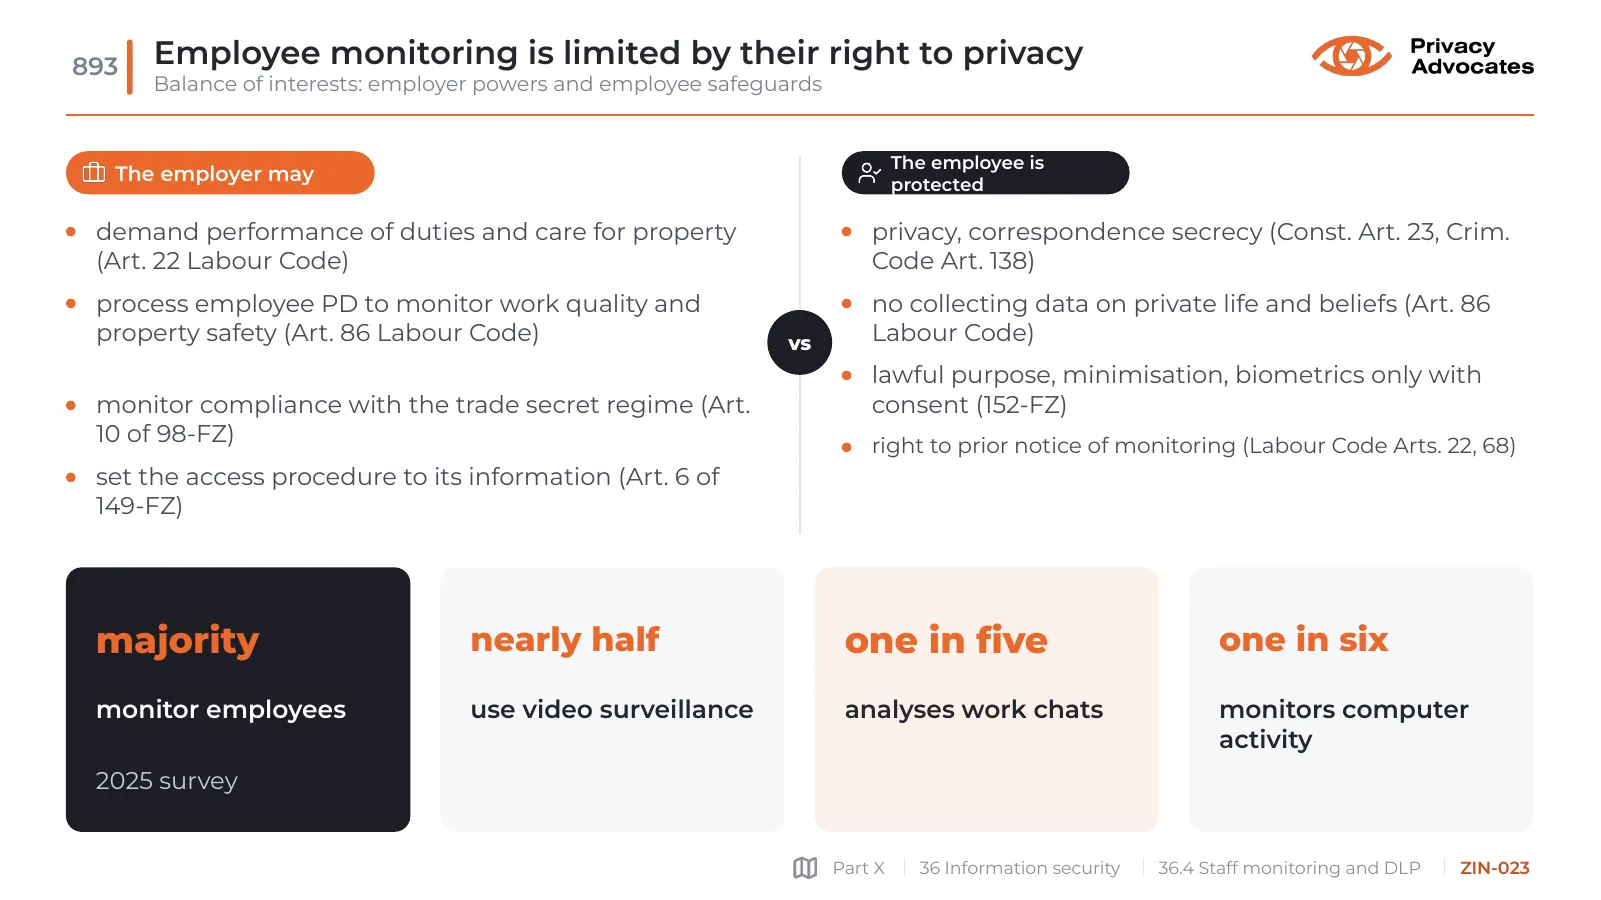
Employee monitoring is limited by their right to privacy

Balance of interests: employer powers and employee safeguards

Slide ZIN-023: Employee monitoring is limited by their right to privacy
Slide text

vs

The employer may

demand performance of duties and care for property (Art. 22 Labour Code)

process employee PD to monitor work quality and property safety (Art. 86 Labour Code)

monitor compliance with the trade secret regime (Art. 10 of 98-FZ)

set the access procedure to its information (Art. 6 of 149-FZ)

The employee is protected

privacy, correspondence secrecy (Const. Art. 23, Crim. Code Art. 138)

no collecting data on private life and beliefs (Art. 86 Labour Code)

lawful purpose, minimisation, biometrics only with consent (152-FZ)

right to prior notice of monitoring (Labour Code Arts. 22, 68)

majority

monitor employees

2025 survey

nearly half

use video surveillance

one in five

analyses work chats

one in six

monitors computer activity

ZIN-024

Monitor the corporate channel, not private messages

Monitoring limits: what is allowed with employee notice and what is banned

Slide ZIN-024: Monitor the corporate channel, not private messages
Slide text

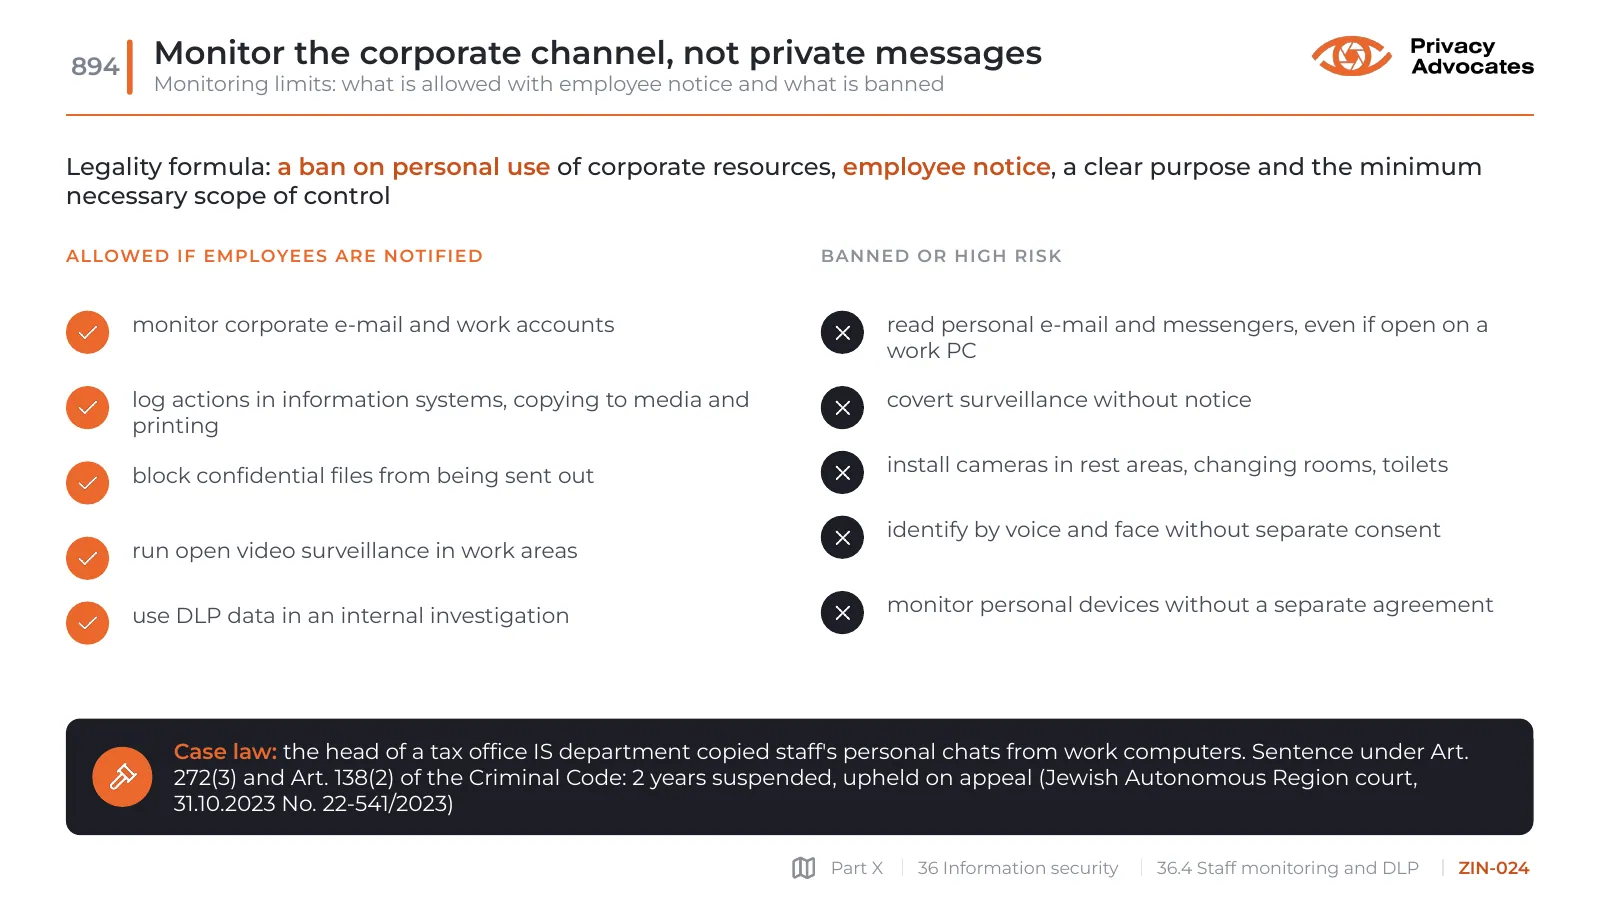
Legality formula: a ban on personal use of corporate resources, employee notice, a clear purpose and the minimum necessary scope of control

Allowed if employees are notified

monitor corporate e-mail and work accounts

log actions in information systems, copying to media and printing

block confidential files from being sent out

run open video surveillance in work areas

use DLP data in an internal investigation

Banned or high risk

read personal e-mail and messengers, even if open on a work PC

covert surveillance without notice

install cameras in rest areas, changing rooms, toilets

identify by voice and face without separate consent

monitor personal devices without a separate agreement

Case law: the head of a tax office IS department copied staff's personal chats from work computers. Sentence under Art. 272(3) and Art. 138(2) of the Criminal Code: 2 years suspended, upheld on appeal (Jewish Autonomous Region court, 31.10.2023 No. 22-541/2023)

ZIN-025

DLP is legalised in six steps before launch

Algorithm: from monitoring purposes to log access

Slide ZIN-025: DLP is legalised in six steps before launch
Slide text
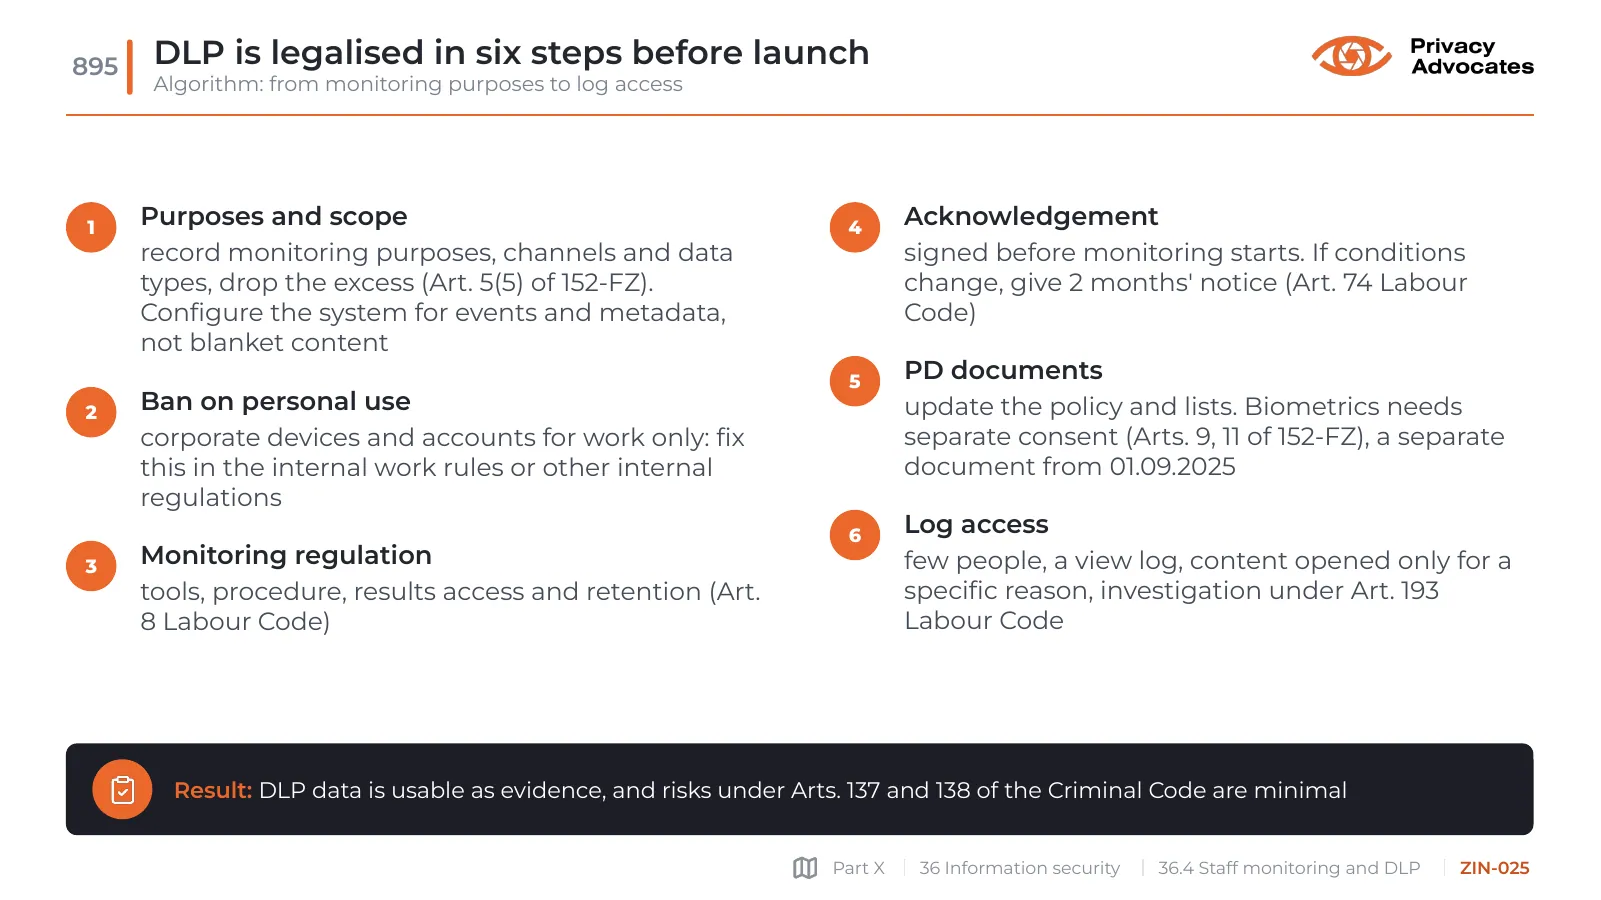
  • 1
  • Purposes and scope

record monitoring purposes, channels and data types, drop the excess (Art. 5(5) of 152-FZ). Configure the system for events and metadata, not blanket content

  • 2
  • Ban on personal use

corporate devices and accounts for work only: fix this in the internal work rules or other internal regulations

  • 3
  • Monitoring regulation

tools, procedure, results access and retention (Art. 8 Labour Code)

  • 4
  • Acknowledgement

signed before monitoring starts. If conditions change, give 2 months' notice (Art. 74 Labour Code)

  • 5
  • PD documents

update the policy and lists. Biometrics needs separate consent (Arts. 9, 11 of 152-FZ), a separate document from 01.09.2025

  • 6
  • Log access

few people, a view log, content opened only for a specific reason, investigation under Art. 193 Labour Code

Result: DLP data is usable as evidence, and risks under Arts. 137 and 138 of the Criminal Code are minimal

ZIN-026

Covert, total monitoring devalues the evidence

Common DLP rollout errors and regulators' 2025 positions

Slide ZIN-026: Covert, total monitoring devalues the evidence
Slide text

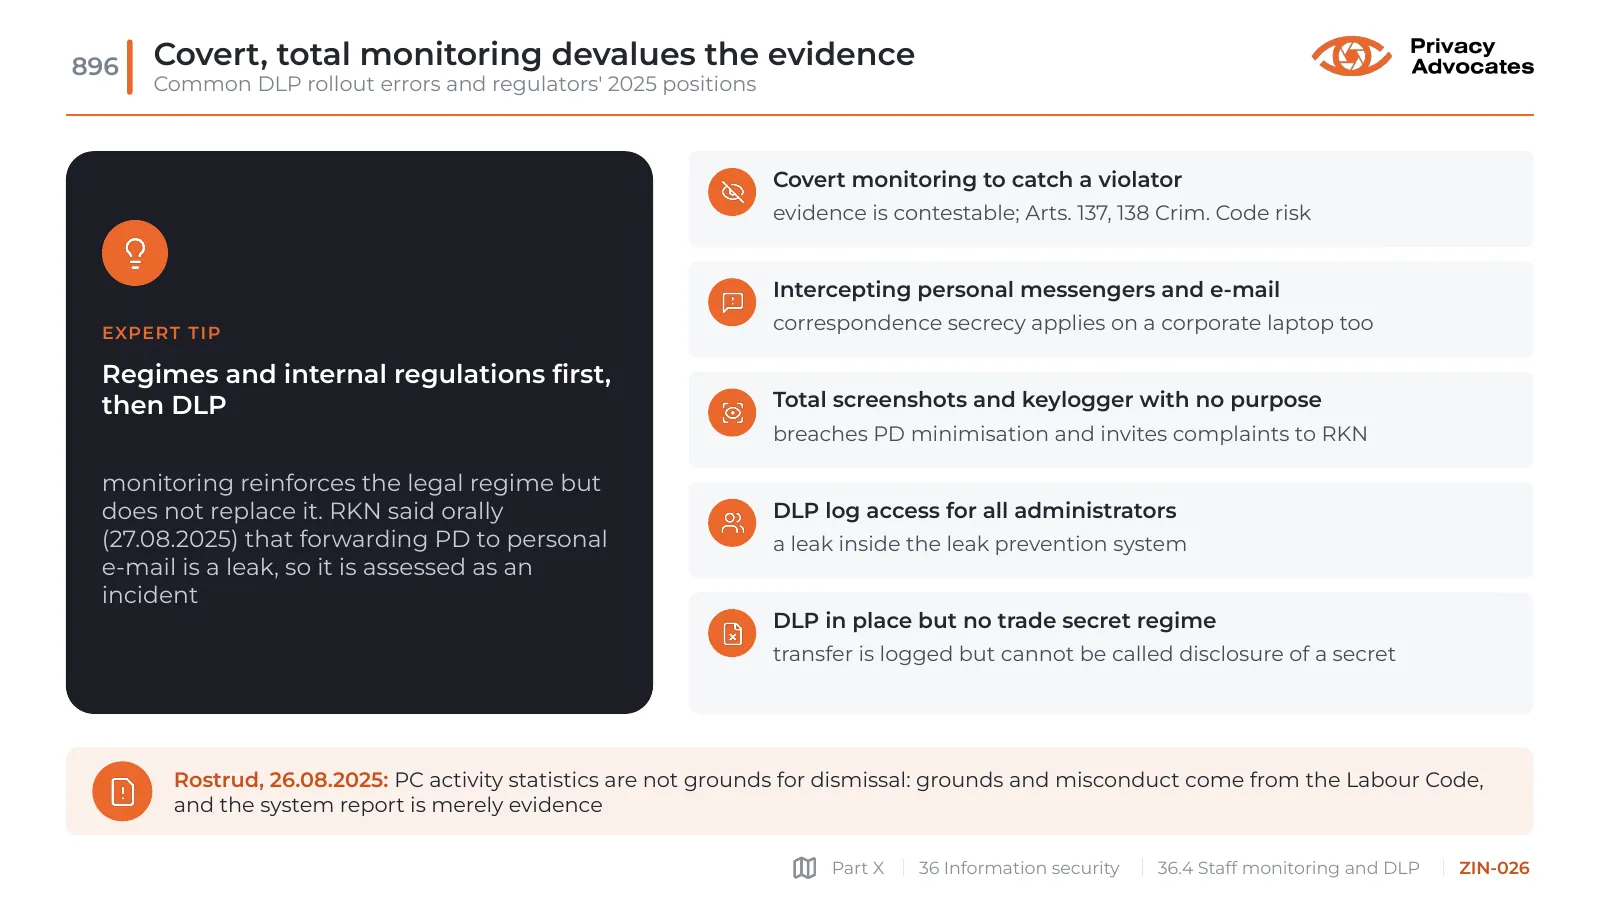
Expert tip

Regimes and internal regulations first, then DLP

monitoring reinforces the legal regime but does not replace it. RKN said orally (27.08.2025) that forwarding PD to personal e-mail is a leak, so it is assessed as an incident

Covert monitoring to catch a violator

evidence is contestable; Arts. 137, 138 Crim. Code risk
Intercepting personal messengers and e-mail

correspondence secrecy applies on a corporate laptop too

Total screenshots and keylogger with no purpose

breaches PD minimisation and invites complaints to RKN

DLP log access for all administrators

a leak inside the leak prevention system

DLP in place but no trade secret regime

transfer is logged but cannot be called disclosure of a secret

Rostrud, 26.08.2025: PC activity statistics are not grounds for dismissal: grounds and misconduct come from the Labour Code, and the system report is merely evidence
36.5

Case solution and sources

ZIN-027

AI drafts the trade secret list, a lawyer checks it

Prompt for drafting the trade secret list and limits of working with the model

Slide ZIN-027: AI drafts the trade secret list, a lawyer checks it
Slide text

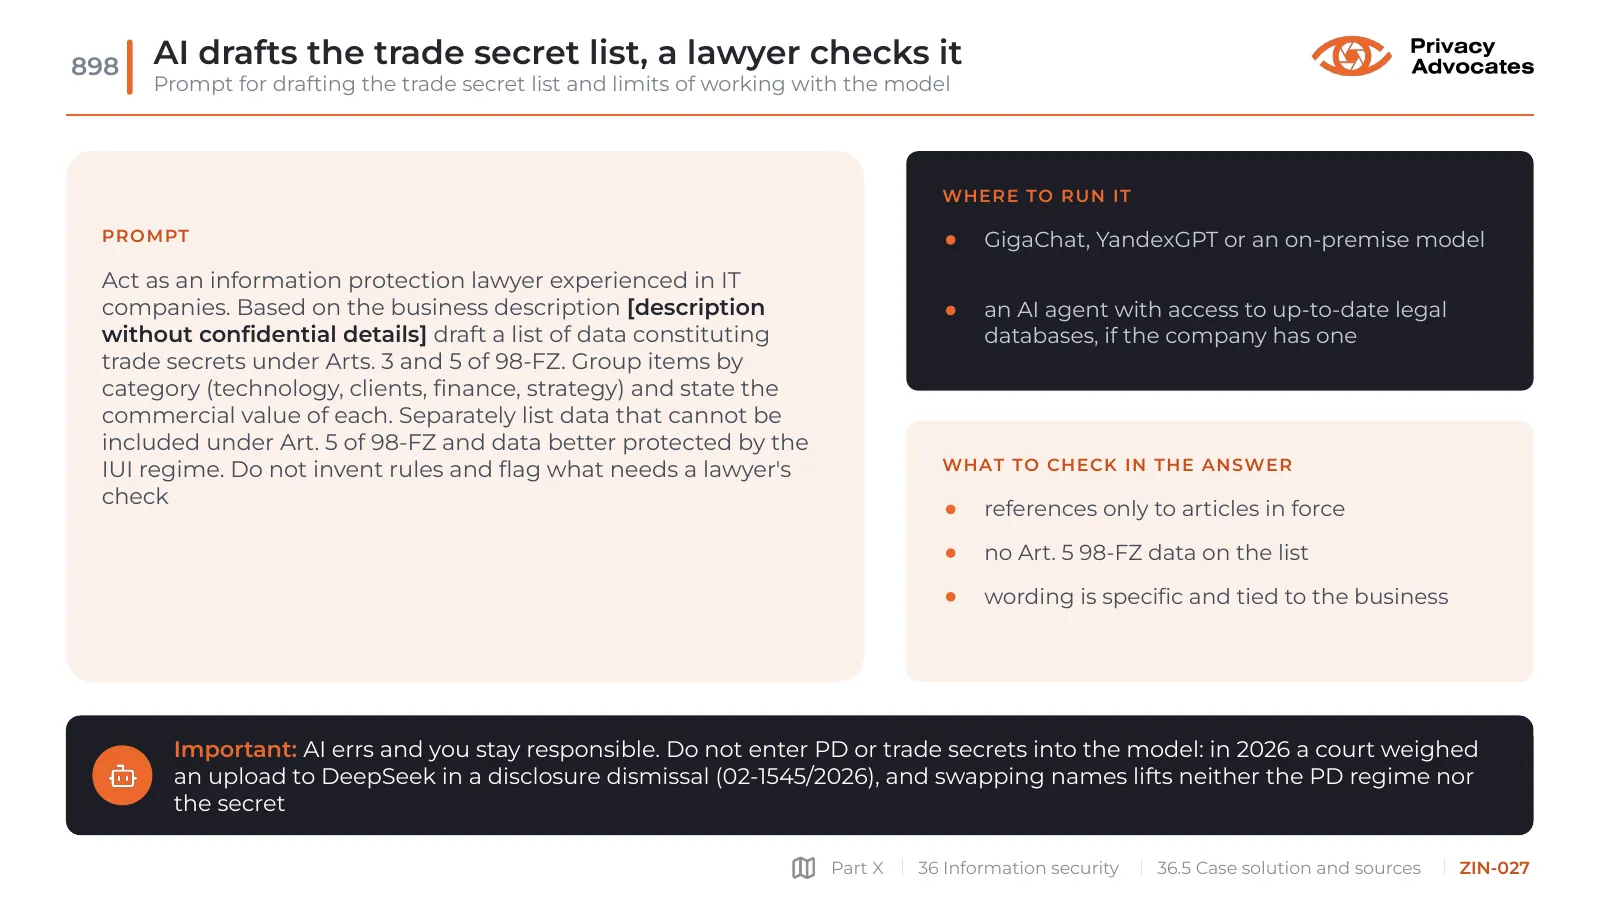
Prompt

Act as an information protection lawyer experienced in IT companies. Based on the business description [description without confidential details] draft a list of data constituting trade secrets under Arts. 3 and 5 of 98-FZ. Group items by category (technology, clients, finance, strategy) and state the commercial value of each. Separately list data that cannot be included under Art. 5 of 98-FZ and data better protected by the IUI regime. Do not invent rules and flag what needs a lawyer's check

Where to run it

GigaChat, YandexGPT or an on-premise model

an AI agent with access to up-to-date legal databases, if the company has one

What to check in the answer

references only to articles in force

no Art. 5 98-FZ data on the list

wording is specific and tied to the business

Important: AI errs and you stay responsible. Do not enter PD or trade secrets into the model: in 2026 a court weighed an upload to DeepSeek in a disclosure dismissal (02-1545/2026), and swapping names lifts neither the PD regime nor the secret

ZIN-028

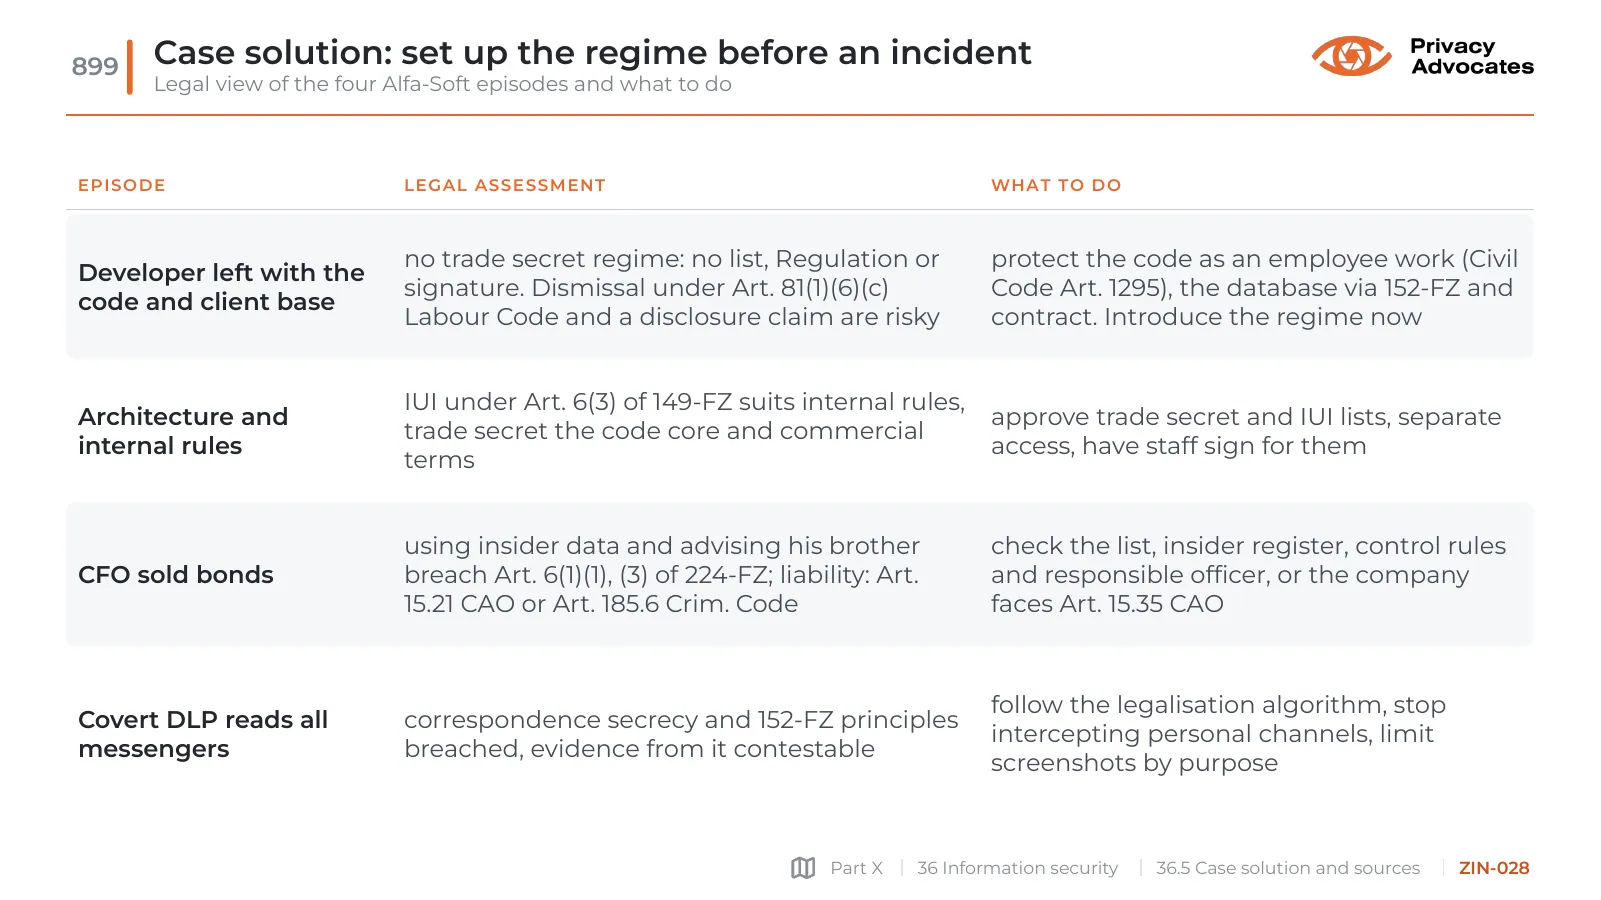
Case solution: set up the regime before an incident

Legal view of the four Alfa-Soft episodes and what to do

Slide ZIN-028: Case solution: set up the regime before an incident
Slide text
  • Episode
  • Legal assessment
  • What to do
  • Developer left with the code and client base
  • no trade secret regime: no list, Regulation or signature. Dismissal under Art. 81(1)(6)(c) Labour Code and a disclosure claim are risky
  • protect the code as an employee work (Civil Code Art. 1295), the database via 152-FZ and contract. Introduce the regime now
  • Architecture and internal rules
  • IUI under Art. 6(3) of 149-FZ suits internal rules, trade secret the code core and commercial terms
  • approve trade secret and IUI lists, separate access, have staff sign for them
  • CFO sold bonds
  • using insider data and advising his brother breach Art. 6(1)(1), (3) of 224-FZ; liability: Art. 15.21 CAO or Art. 185.6 Crim. Code
  • check the list, insider register, control rules and responsible officer, or the company faces Art. 15.35 CAO

Covert DLP reads all messengers

correspondence secrecy and 152-FZ principles breached, evidence from it contestable
follow the legalisation algorithm, stop intercepting personal channels, limit screenshots by purpose

ZIN-029

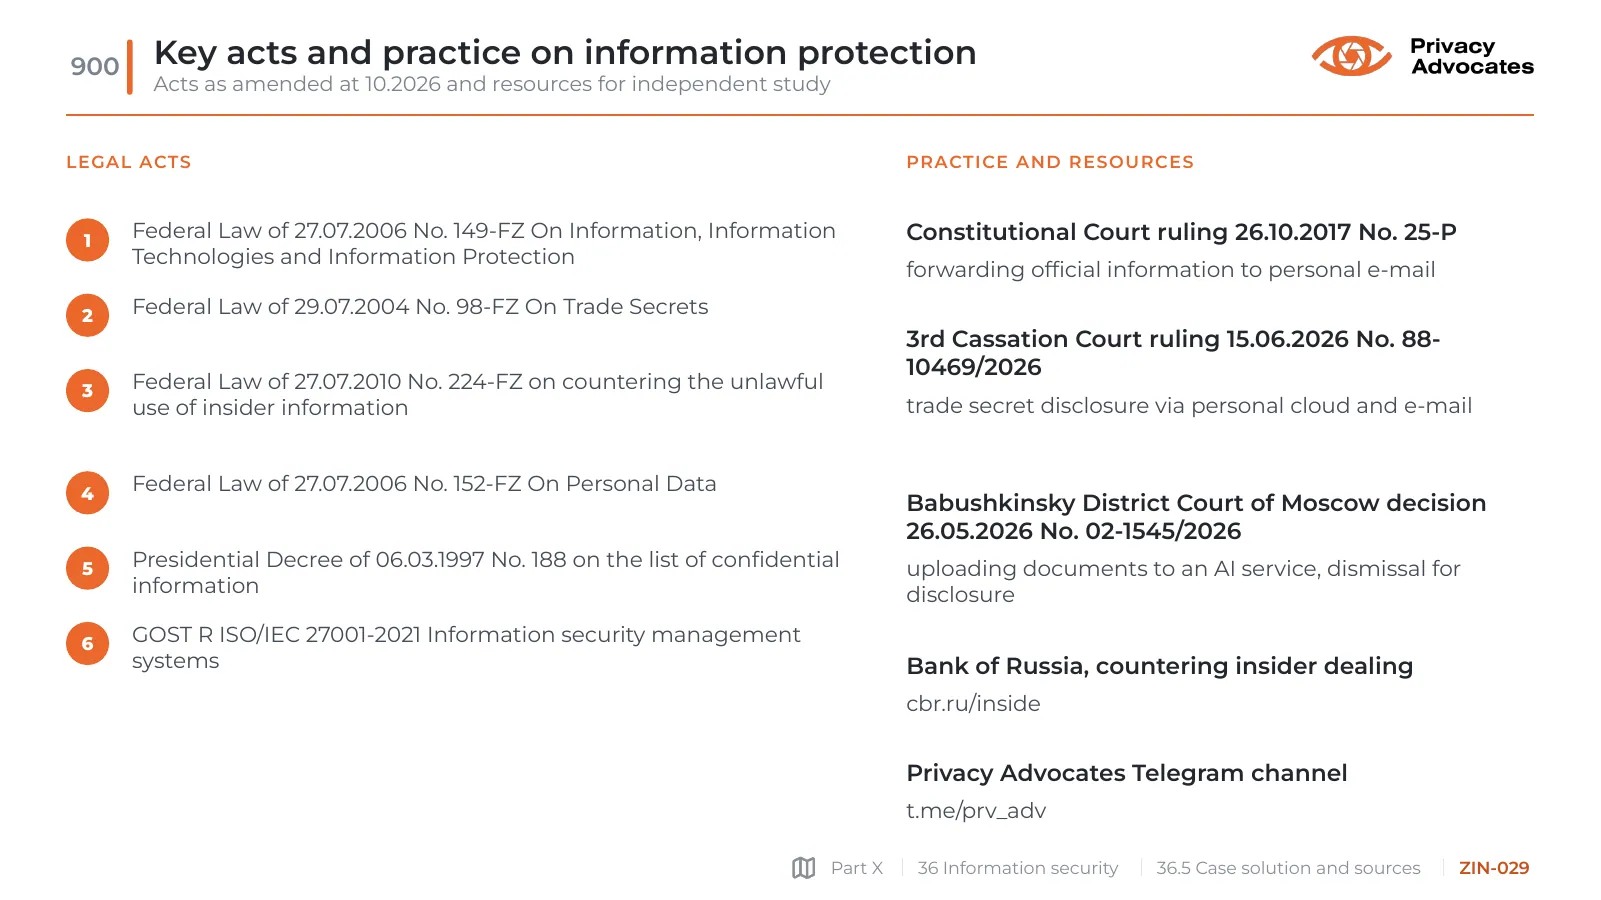
Key acts and practice on information protection

Acts as amended at 10.2026 and resources for independent study

Slide ZIN-029: Key acts and practice on information protection
Slide text

Legal acts

  • 1
  • Federal Law of 27.07.2006 No. 149-FZ On Information, Information Technologies and Information Protection
  • 2
  • Federal Law of 29.07.2004 No. 98-FZ On Trade Secrets
  • 3
  • Federal Law of 27.07.2010 No. 224-FZ on countering the unlawful use of insider information
  • 4
  • Federal Law of 27.07.2006 No. 152-FZ On Personal Data
  • 5
  • Presidential Decree of 06.03.1997 No. 188 on the list of confidential information
  • 6
  • GOST R ISO/IEC 27001-2021 Information security management systems

Practice and resources

Constitutional Court ruling 26.10.2017 No. 25-P

forwarding official information to personal e-mail

3rd Cassation Court ruling 15.06.2026 No. 88-10469/2026

trade secret disclosure via personal cloud and e-mail

Babushkinsky District Court of Moscow decision 26.05.2026 No. 02-1545/2026

uploading documents to an AI service, dismissal for disclosure

Bank of Russia, countering insider dealing

cbr.ru/inside

Privacy Advocates Telegram channel

t.me/prv_adv

36.6

Correspondence and secrecy of communications

ZIN-030

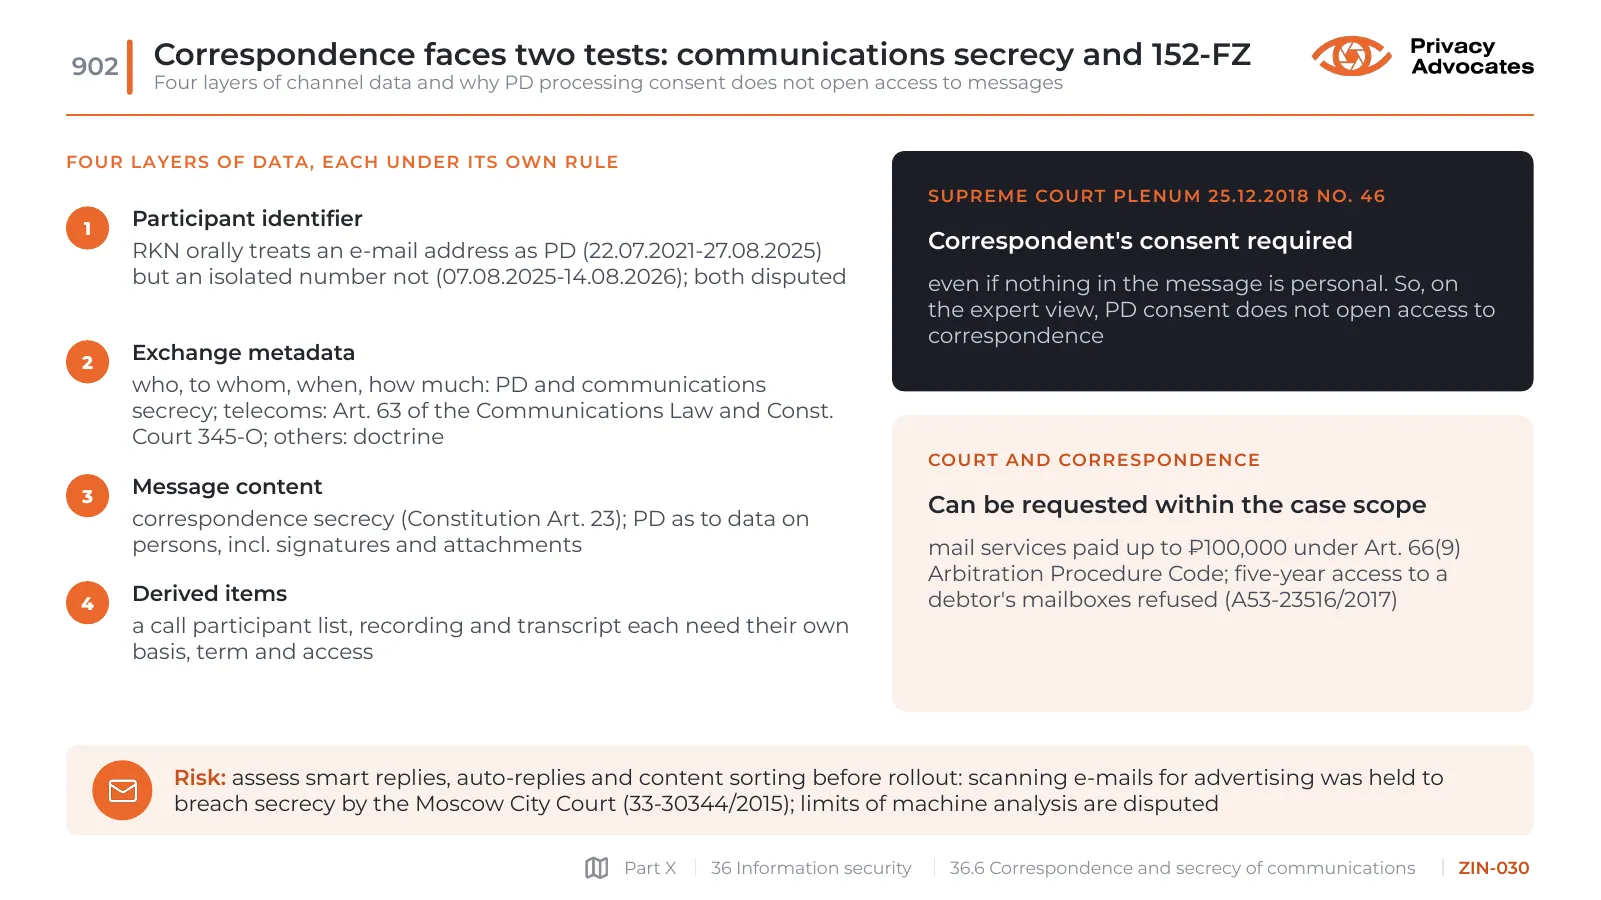
Correspondence faces two tests: communications secrecy and 152-FZ

Four layers of channel data and why PD processing consent does not open access to messages

Slide ZIN-030: Correspondence faces two tests: communications secrecy and 152-FZ
Slide text

Four layers of data, each under its own rule

  • 1
  • Participant identifier

RKN orally treats an e-mail address as PD (22.07.2021-27.08.2025) but an isolated number not (07.08.2025-14.08.2026); both disputed

  • 2
  • Exchange metadata

who, to whom, when, how much: PD and communications secrecy; telecoms: Art. 63 of the Communications Law and Const. Court 345-O; others: doctrine

  • 3
  • Message content

correspondence secrecy (Constitution Art. 23); PD as to data on persons, incl. signatures and attachments

  • 4
  • Derived items

a call participant list, recording and transcript each need their own basis, term and access

Supreme Court Plenum 25.12.2018 No. 46

Correspondent's consent required

even if nothing in the message is personal. So, on the expert view, PD consent does not open access to correspondence

Court and correspondence

Can be requested within the case scope

mail services paid up to ₽100,000 under Art. 66(9) Arbitration Procedure Code; five-year access to a debtor's mailboxes refused (A53-23516/2017)

Risk: assess smart replies, auto-replies and content sorting before rollout: scanning e-mails for advertising was held to breach secrecy by the Moscow City Court (33-30344/2015); limits of machine analysis are disputed

ZIN-031

Two separate bans restrict work with foreign messengers

Art. 10(8) of 149-FZ and Art. 15 of 41-FZ differ in persons, actions and list; sanction Art. 13.11.2 CAO

Slide ZIN-031: Two separate bans restrict work with foreign messengers
Slide text
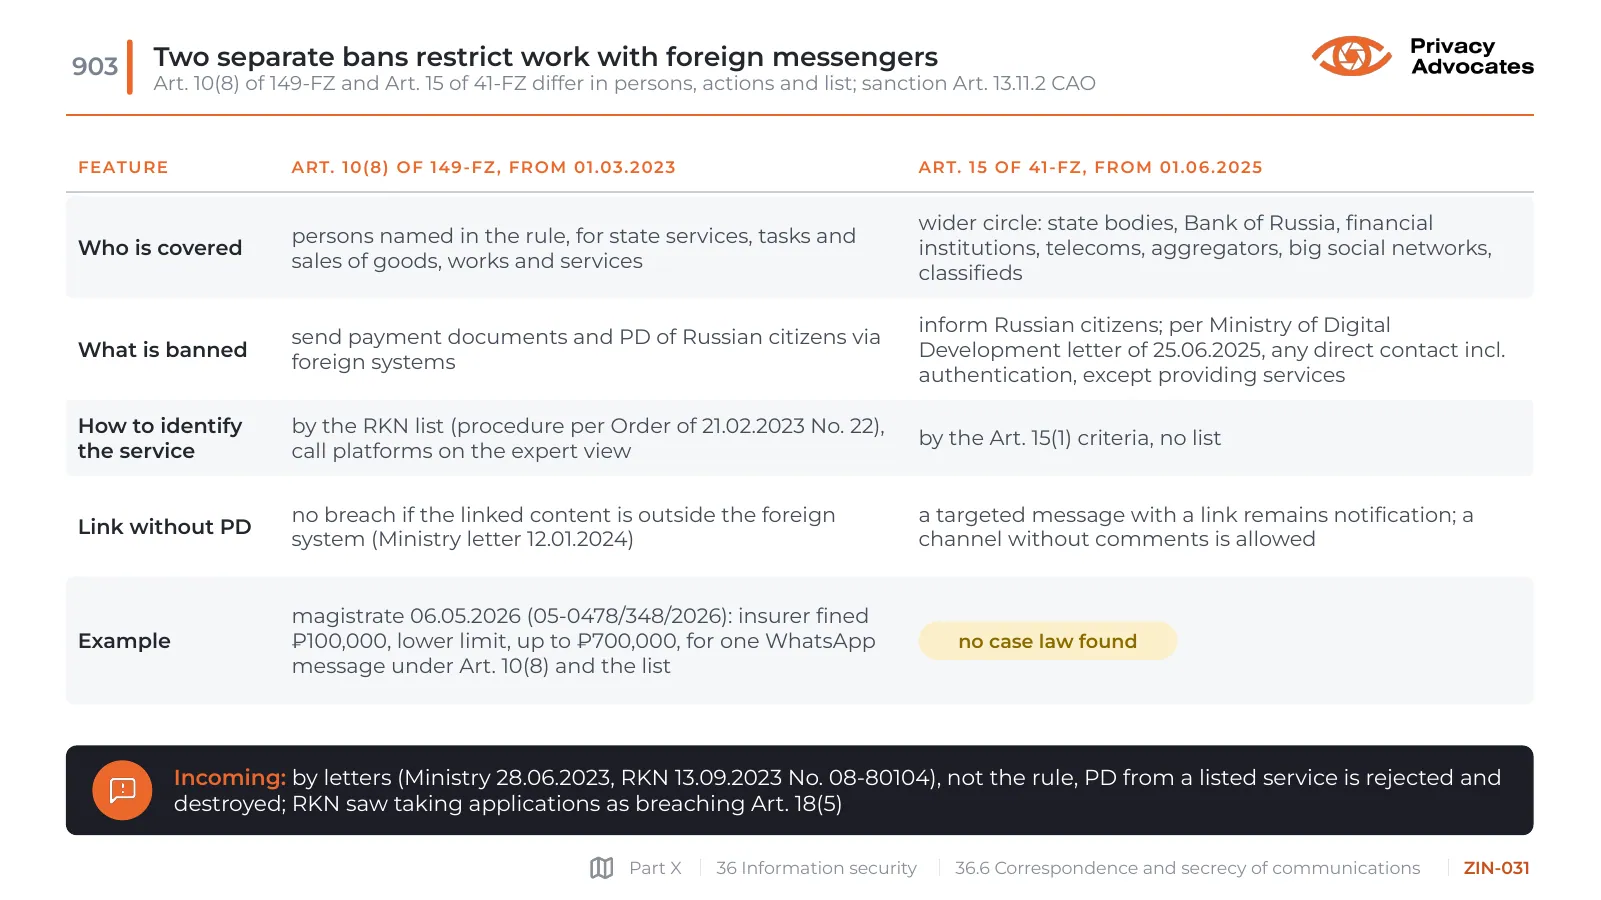
  • Feature
  • Art. 10(8) of 149-FZ, from 01.03.2023
  • Art. 15 of 41-FZ, from 01.06.2025
  • Who is covered
  • persons named in the rule, for state services, tasks and sales of goods, works and services
  • wider circle: state bodies, Bank of Russia, financial institutions, telecoms, aggregators, big social networks, classifieds
  • What is banned
  • send payment documents and PD of Russian citizens via foreign systems
  • inform Russian citizens; per Ministry of Digital Development letter of 25.06.2025, any direct contact incl. authentication, except providing services
  • How to identify the service
  • by the RKN list (procedure per Order of 21.02.2023 No. 22), call platforms on the expert view
  • by the Art. 15(1) criteria, no list
  • Link without PD
  • no breach if the linked content is outside the foreign system (Ministry letter 12.01.2024)
  • a targeted message with a link remains notification; a channel without comments is allowed
  • Example
  • magistrate 06.05.2026 (05-0478/348/2026): insurer fined ₽100,000, lower limit, up to ₽700,000, for one WhatsApp message under Art. 10(8) and the list
  • no case law found

Incoming: by letters (Ministry 28.06.2023, RKN 13.09.2023 No. 08-80104), not the rule, PD from a listed service is rejected and destroyed; RKN saw taking applications as breaching Art. 18(5)

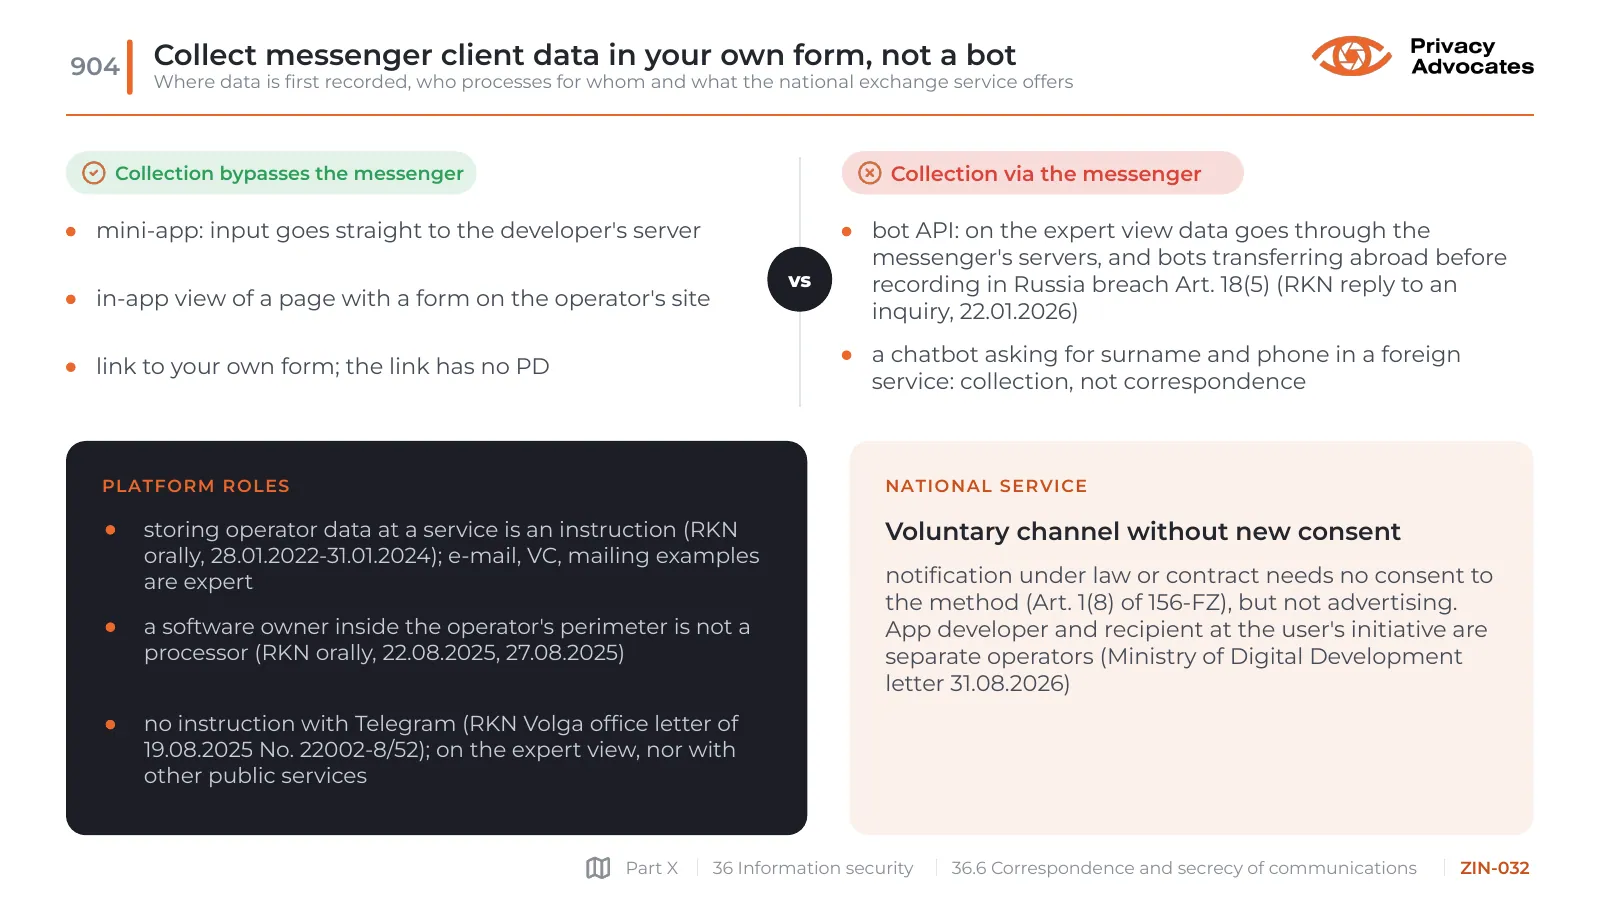
ZIN-032

Collect messenger client data in your own form, not a bot

Where data is first recorded, who processes for whom and what the national exchange service offers

Slide ZIN-032: Collect messenger client data in your own form, not a bot
Slide text

vs

Collection bypasses the messenger

mini-app: input goes straight to the developer's server

in-app view of a page with a form on the operator's site

link to your own form; the link has no PD

Collection via the messenger

bot API: on the expert view data goes through the messenger's servers, and bots transferring abroad before recording in Russia breach Art. 18(5) (RKN reply to an inquiry, 22.01.2026)

a chatbot asking for surname and phone in a foreign service: collection, not correspondence

Platform roles

storing operator data at a service is an instruction (RKN orally, 28.01.2022-31.01.2024); e-mail, VC, mailing examples are expert

a software owner inside the operator's perimeter is not a processor (RKN orally, 22.08.2025, 27.08.2025)

no instruction with Telegram (RKN Volga office letter of 19.08.2025 No. 22002-8/52); on the expert view, nor with other public services

National service

Voluntary channel without new consent

notification under law or contract needs no consent to the method (Art. 1(8) of 156-FZ), but not advertising. App developer and recipient at the user's initiative are separate operators (Ministry of Digital Development letter 31.08.2026)

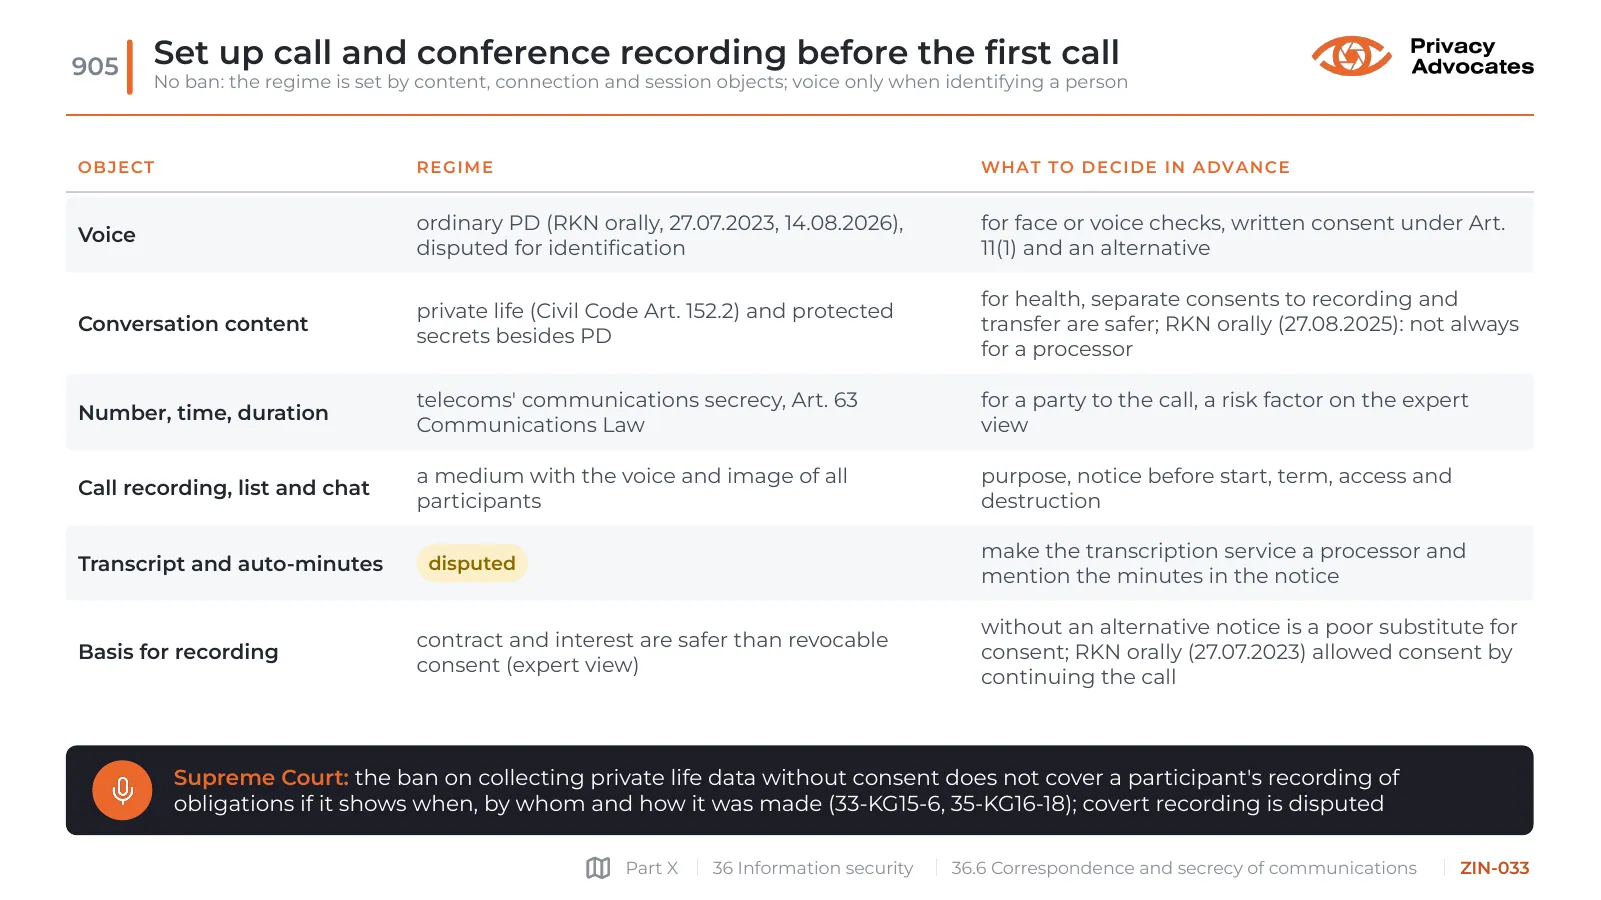
ZIN-033

Set up call and conference recording before the first call

No ban: the regime is set by content, connection and session objects; voice only when identifying a person

Slide ZIN-033: Set up call and conference recording before the first call
Slide text
  • Object
  • Regime
  • What to decide in advance
  • Voice
  • ordinary PD (RKN orally, 27.07.2023, 14.08.2026), disputed for identification
  • for face or voice checks, written consent under Art. 11(1) and an alternative
  • Conversation content
  • private life (Civil Code Art. 152.2) and protected secrets besides PD
  • for health, separate consents to recording and transfer are safer; RKN orally (27.08.2025): not always for a processor
  • Number, time, duration
  • telecoms' communications secrecy, Art. 63 Communications Law
  • for a party to the call, a risk factor on the expert view
  • Call recording, list and chat
  • a medium with the voice and image of all participants
  • purpose, notice before start, term, access and destruction
  • Transcript and auto-minutes
  • disputed
  • make the transcription service a processor and mention the minutes in the notice
  • Basis for recording
  • contract and interest are safer than revocable consent (expert view)
  • without an alternative notice is a poor substitute for consent; RKN orally (27.07.2023) allowed consent by continuing the call

Supreme Court: the ban on collecting private life data without consent does not cover a participant's recording of obligations if it shows when, by whom and how it was made (33-KG15-6, 35-KG16-18); covert recording is disputed

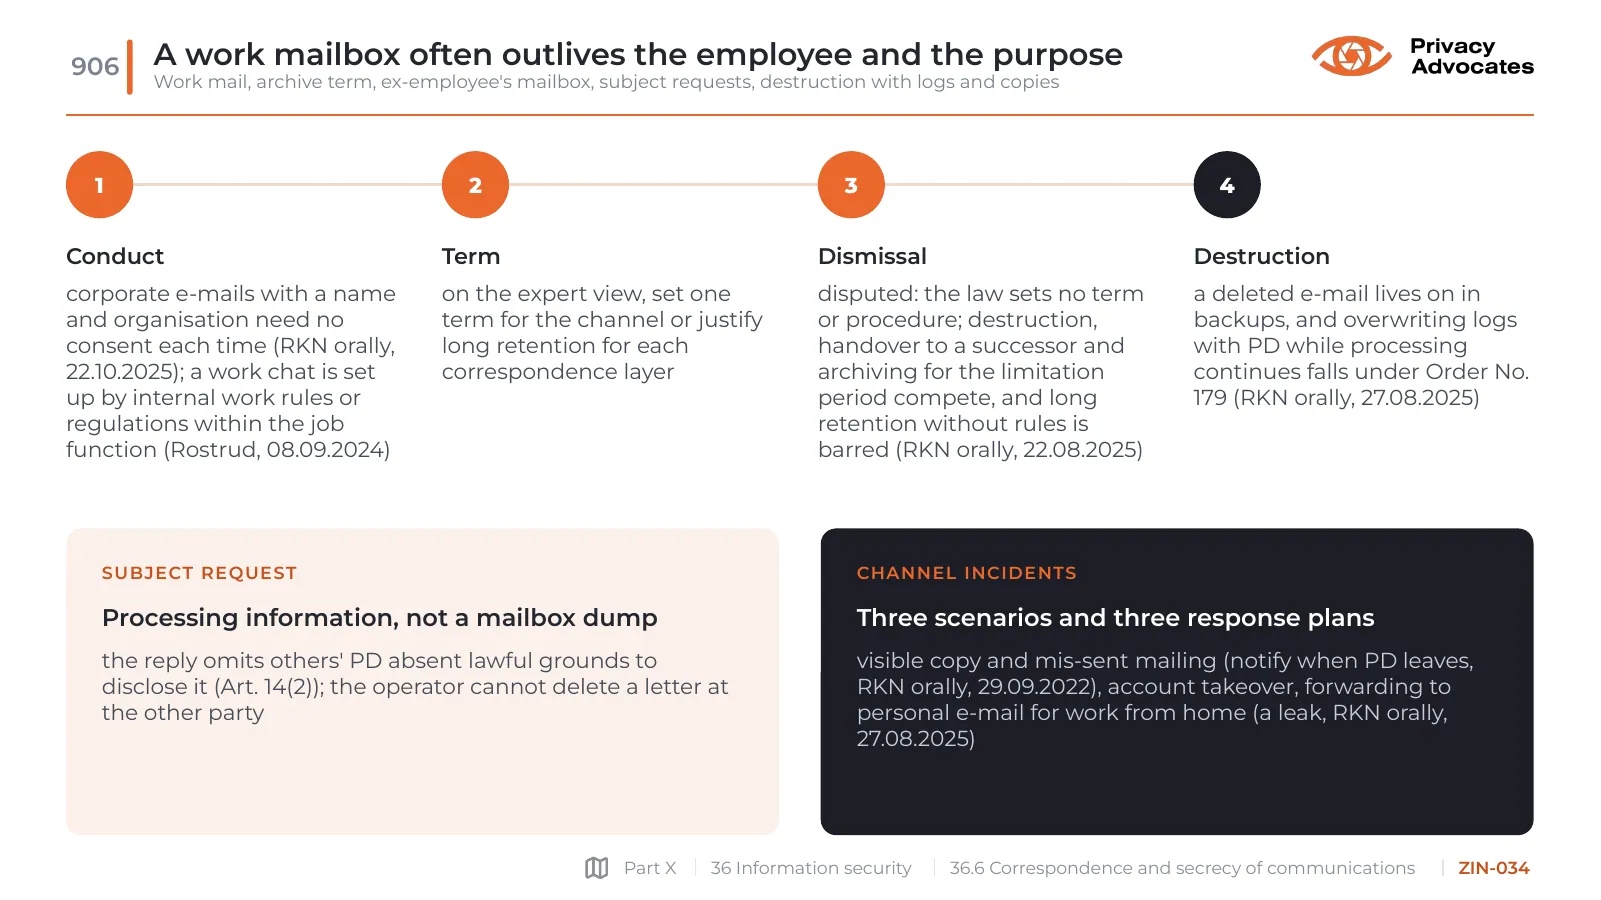
ZIN-034

A work mailbox often outlives the employee and the purpose

Work mail, archive term, ex-employee's mailbox, subject requests, destruction with logs and copies

Slide ZIN-034: A work mailbox often outlives the employee and the purpose
Slide text

1

Conduct

corporate e-mails with a name and organisation need no consent each time (RKN orally, 22.10.2025); a work chat is set up by internal work rules or regulations within the job function (Rostrud, 08.09.2024)

2

Term

on the expert view, set one term for the channel or justify long retention for each correspondence layer

3

Dismissal

disputed: the law sets no term or procedure; destruction, handover to a successor and archiving for the limitation period compete, and long retention without rules is barred (RKN orally, 22.08.2025)

4

Destruction

a deleted e-mail lives on in backups, and overwriting logs with PD while processing continues falls under Order No. 179 (RKN orally, 27.08.2025)

Subject request

Processing information, not a mailbox dump

the reply omits others' PD absent lawful grounds to disclose it (Art. 14(2)); the operator cannot delete a letter at the other party

Channel incidents

Three scenarios and three response plans

visible copy and mis-sent mailing (notify when PD leaves, RKN orally, 29.09.2022), account takeover, forwarding to personal e-mail for work from home (a leak, RKN orally, 27.08.2025)

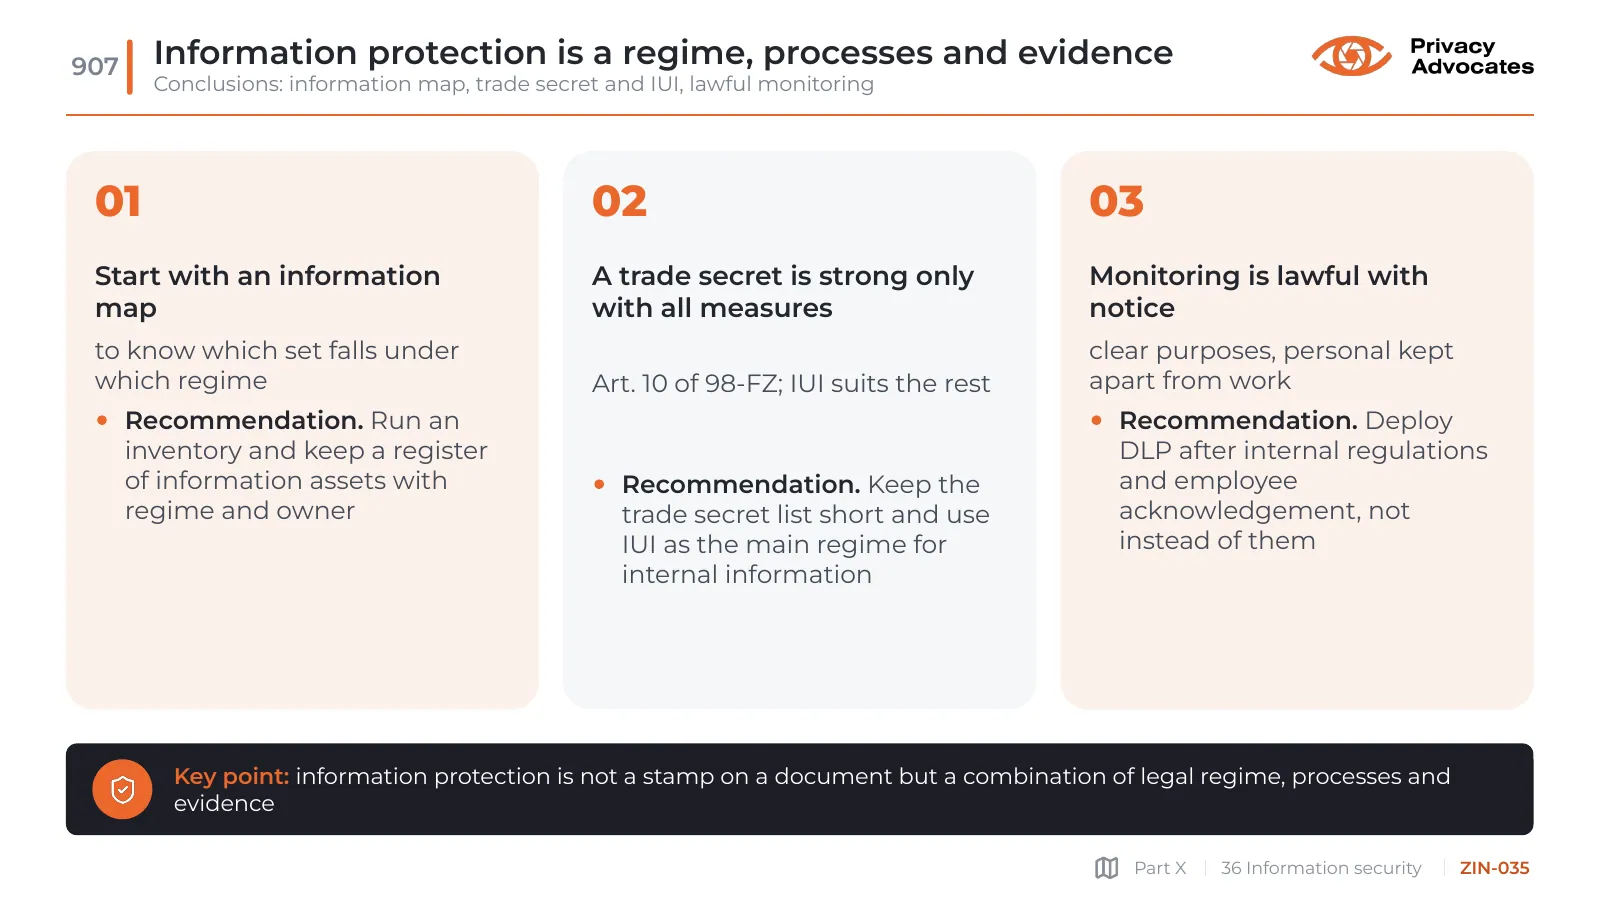
ZIN-035

Information protection is a regime, processes and evidence
Conclusions: information map, trade secret and IUI, lawful monitoring

Slide ZIN-035: Information protection is a regime, processes and evidence
Slide text

01

Start with an information map

to know which set falls under which regime

Recommendation. Run an inventory and keep a register of information assets with regime and owner

02

A trade secret is strong only with all measures

Art. 10 of 98-FZ; IUI suits the rest

Recommendation. Keep the trade secret list short and use IUI as the main regime for internal information

03

Monitoring is lawful with notice

clear purposes, personal kept apart from work

Recommendation. Deploy DLP after internal regulations and employee acknowledgement, not instead of them

Key point: information protection is not a stamp on a document but a combination of legal regime, processes and evidence